Database Operations GovernanceDatabase Operations Governance

Onay tamamlanmadan çalıştırma açılmaz. Hassas kolonlar maskelenmeden veri teslim edilmez. Kanıt tek dosyada durur.Execution does not open until approval completes. Data is not delivered until sensitive columns are masked. The evidence sits in one file. SQL Change Guard; SQL Server, PostgreSQL ve Oracle üzerinde çalışacak her betiği ve üretim verisine yönelik her talebi tek bir onay, risk ve denetim döngüsüne bağlar.SQL Change Guard binds every script bound for SQL Server, PostgreSQL or Oracle, and every request for production data, into one approval, risk and audit loop.

DeğişiklikChange Betik ayrıştırılır, riski hesaplanır, politikanın gerektirdiği onaylardan geçer, kontrollü çalışır. The script is parsed, its risk is set, it passes the approvals the policy requires and then runs under control.
ErişimAccess Üretimden veri okuma talebe bağlanır, hassas kolonlar maskelenir, sonuç şifreli paketle teslim edilir. Reading production data is tied to a request, sensitive columns are masked and the result is delivered in an encrypted package.
KanıtEvidence Kim istedi, kim onayladı, ne çalıştı sorusunun cevabı mühürlü tek dosyada denetçiye verilir. Who asked, who approved and what ran is handed to the auditor as one sealed file.
SQL Server PostgreSQL Oracle

Bu üç veritabanı yönetilen hedef sistemlerdir. Ürünün kendi kayıt veritabanı SQL Server üzerinde çalışır. These three are the managed target systems. The product keeps its own records on SQL Server.

88 SQL kuralı, her biri açılıp kapatılabilirSQL rules, each can be switched on or off
5 risk bandı: Bilgi, Düşük, Orta, Yüksek, Kritikrisk bands: Info, Low, Medium, High, Critical
31 hazır rapor, beş gruptabuilt in reports, in five groups
3 bağımsız denetim katmanıindependent audit layers
En sık duyduğumuz cümleThe sentence we hear most

"Bizde bu süreç zaten var.""We already have this process."

Büyük ihtimalle doğru. Değişiklik yönetimi, onay akışı ve dağıtım hattı çoğu kurumda gerçekten çalışıyor. Aşağıdaki üç soru, o sürecin tam olarak nerede bittiğini gösterir.It is probably true. Change management, approvals and a delivery pipeline really do work in most organisations. These three questions show exactly where that process ends.

Geçen ay üretimde çalışan SQL ifadelerinin yüzde kaçı sürecinizden geçti?What share of the SQL statements that ran in production last month went through your process?

Dağıtım hattı taşıdığını bilir, taşımadığı hakkında sessizdir. Sessizlik "hiçbir şey olmadı" diye okunur. Bu oranı hesaplayan bir yer yoksa cevap tahmindir.A pipeline knows what it carried and stays silent about what it did not. Silence reads as "nothing happened". If no system computes this share, the answer is a guess.

Üretimden en son çekilen müşteri listesi kimin bilgisayarında, hangi gerekçeyle ve hangi kolonlarla çekildi?The last customer list pulled from production: whose machine is it on, on what stated basis, and with which columns?

Değişiklik tarafı yönetiliyor olabilir. Okuma tarafı çoğu kurumda hiç yönetilmiyor. Kişisel veri de en çok oradan çıkıyor.The change side may well be governed. The read side is usually not governed at all, and that is where personal data leaves.

Geçen çeyrekte kaç değişiklik talebi reddedildi?How many change requests were rejected last quarter?

Cevap sıfırsa kontrol eleme yapmıyor demektir. Onay, hayır diyebildiği ölçüde onaydır ve reddin kaydı denetimde ayrıca sorulur.If the answer is zero, the control is filtering nothing. An approval is only an approval to the extent that it can say no, and auditors ask for the record of rejections separately.

Bu üç sorunun cevabı bilet sisteminizde, dağıtım hattınızda veya veritabanı günlüğünüzde durmuyor. Hiçbirinin görev tanımında değil. SQL Change Guard tam olarak bu üç soruyu cevaplamak için var.The answers to these three questions do not live in your ticketing system, your pipeline or your database log. They fall outside every one of those remits. SQL Change Guard exists to answer exactly these three.

SQL Change Guard nedirWhat SQL Change Guard is

Kurumunuzun kendi ağına kurulan bir yönetişim katmanıdır. Üretim veritabanlarınız ile onlara dokunan insanlar arasında durur. Çalıştırılacak her betiği ve üretimden veri isteyen her talebi, iş gerçekleşmeden önce yazılı bir kurala göre değerlendirir, politikanın gerektirdiği onaylardan geçirir ve geriye sonradan kanıtlanabilir tek bir kayıt bırakır. Bu yaklaşımın adı Database Operations Governance: yalnız veritabanı değişikliğini değil, üretim verisine erişimi de aynı çatı altında ele alır.It is a governance layer installed inside your own network. It sits between your production databases and the people who touch them. Every script that will run and every request for production data is assessed against a written rule before the work happens, passed through the approvals the policy requires, and left behind as one record that can be proved later. The name for this approach is Database Operations Governance: it covers not only database change but production data access under the same roof.

Kimin için: üretim veritabanlarında değişiklik ve veri erişimi kararlarının kayıtlı olması gereken kurumlar. Şu dört soruyla kendinizi ölçebilirsiniz.Who it is for: organisations that need change and data access decisions on production databases to be on the record. Four questions let you measure yourself.

İkisine "hayır" diyorsanız bu katman sizin için. Dördüne birden "evet" diyebiliyorsanız zaten kurmuşsunuz demektir.If two of them are a no, this layer is for you. If all four are a yes, you have already built it.

Ne değildir: dağıtım aracı değildir, bilet sistemi değildir, izleme ürünü değildir, veritabanı yönetim aracı değildir. Jira, ServiceNow, CI/CD hattınız, Liquibase ve log platformunuz yerinde kalır. Bu katman onların yerine geçmez; hiçbirinin görev tanımında olmayan soruyu cevaplar.What it is not: not a deployment tool, not a ticketing system, not a monitoring product, not a database administration tool. Jira, ServiceNow, your CI/CD pipeline, Liquibase and your log platform all stay where they are. This layer does not replace them; it answers the question that falls outside every one of their remits.

Kontrol eksik değil, kontroller birbirinden habersizControls are not missing. They just do not know about each other.

Değişiklik yönetimi var. Onay akışı var. CI/CD var. Log var. Yılda iki kez denetim var. Hepsi çalışıyor, hepsi ayrı sistemde.

Change management is in place. Approvals are in place. CI/CD is in place. Logging is in place. An audit happens twice a year. All of it works, and all of it lives in a different system.

Değişiklik onayı bir sistemde, veri erişimi başka bir sistemde, denetim kanıtı üçüncü bir sistemde. Denetçi geldiğinde altı ayrı yerden ekran görüntüsü toplanıyor.

Change approval lives in one system, data access in another, audit evidence in a third. When the auditor arrives, screenshots are collected from six places.

Kimse yanlış bir şey yapmadı. Sadece hiç kimse bütünün sahibi değil.

Nobody did anything wrong. It is just that nobody owns the whole.

Denetim sabahıThe morning of the audit

"Salı günü 14:00'te üretimde bu tabloyu kim değiştirdi ve kim onayladı?""Who changed this table in production at 14:00 on Tuesday, and who approved it?"

Cevap kurumda vardır. Sorun, cevabın dört ayrı sistemde parça parça durmasıdır. Her parçayı elle eşleştirmek zaman alır ve bu süre her denetimde yeniden ödenir.The answer exists inside the organisation. The problem is that it sits in four separate systems in pieces. Matching those pieces by hand takes time, and that time is paid again at every audit.

Bugünkü kurulumToday's setup

Dört sistem, dört yarım cevapFour systems, four half answers

  • Bilet sistemiTicketing Neyin istendiğini söyler. Betiğin son halini bilmez. Says what was asked for. It does not know the final text of the script.
  • Dağıtım hattıDelivery pipeline Neyin taşındığını söyler. Hattın dışından gelen işi hiç görmez. Says what it carried. It never sees work that arrives outside the pipeline.
  • Veritabanı günlüğüDatabase logging Ne çalıştığını söyler. Neden çalıştığını ve kimin izin verdiğini söylemez. Says what ran. It does not say why it ran or who allowed it.
  • E-posta ve sohbetEmail and chat Kararın gerçekte verildiği yer burasıdır ve kanıt olarak kabul edilmez. This is where the decision was actually taken, and it does not count as evidence.

Korelasyon vergisi:The correlation tax: Tek bir soruya cevap vermek için dört sistemin zaman damgalarını elle eşleştirmek gerekir. Bu emek denetim başına ödenir, kanıt olarak ekran görüntüsü bırakır ve eşleşme hiçbir zaman tam olmaz. Answering a single question means lining up timestamps across four systems by hand. That effort is paid per audit, it leaves screenshots as evidence, and the match is never complete.

SQL Change Guard

Tek kayıt, tam cevapOne record, the whole answer

  • Talep ve biletRequest and ticket Betik, hedef sunucular ve kurumun biçim kuralına uyan bilet numarası aynı kayıtta. The script, the target servers and a ticket number matching your format rule, in one record.
  • Karar ve kuralDecision and rule Riski hangi kural belirledi, hangi politika hangi onayı istedi, kim onayladı. Which rule set the risk, which policy demanded which approval, and who approved.
  • ÇalıştırmaExecution Çalışan metnin parmak izi, hangi sunucuda, ne zaman, kimin başlattığı ve sonucu. The fingerprint of the text that ran, on which server, when, who started it and the outcome.
  • KanıtEvidence Tüm yaşam döngüsü mühürlü tek dosya olarak dışa aktarılır ve bağımsız doğrulanır. The whole lifecycle exports as one sealed file that can be verified independently.

Sonuç:The outcome: Denetçinin sorusu bir talep numarasına iner. Kanıt işin kendisinden üretilir, denetim için ayrıca hazırlanmaz. The auditor's question comes down to one request number. The evidence is produced by the work itself rather than prepared for the audit.

Denetçinin sorusuThe auditor asks Dağınık kurulumda cevabı neredeWhere the answer lives when tooling is scattered SQL Change Guard ileWith SQL Change Guard
Bu değişikliği kim istedi?Who asked for this change? Bilet sisteminde, betiğin son haline bağlı değilIn the ticket, not linked to the final script Talep kaydında, betikle birlikteOn the request, together with the script
Hangi kural gereği onaya gitti?Under which rule did it go for approval? Çoğu zaman hiçbir yerde, alışkanlığa bağlıUsually nowhere; it follows habit Talebe dondurulmuş o günkü kural setiThe rule set of that day, frozen onto the request
Çalışan metin onaylanan metin miydi?Was the text that ran the text that was approved? Karşılaştırma elle yapılır, çoğu zaman yapılmazCompared by hand, and usually not at all Betiğin parmak izi kayıtta dururThe script fingerprint stays on the record
Üretim verisini kim, hangi gerekçeyle okudu?Who read production data, and why? Erişim izleme aracında; gerekçe sohbetteIn the activity monitor; the reason is in a chat thread Sorgu talebinde: gerekçe, maskeleme kararı ve teslim adresiOn the query request: the reason, the masking decision and the delivery address
Kaydın kendisi değiştirilmiş olabilir mi?Could the record itself have been altered? Kaydı tutan ekibin yetkisine güvenilirIt rests on trusting the team that keeps the record İmzalı iz, ayrı veritabanında mühürlü kopya ve doğrulama düğmesiA signed trail, a sealed copy in a separate database and a verify action
İki ayrı akışTwo separate flows

Üretime giden iki yol, aynı yönetişim modeliTwo paths into production, one governance model

Bir şeyi değiştirmek ile bir şeyi okumak farklı risklerdir. Ürün ikisini ayrı akış olarak yönetir.Changing something and reading something are different risks. The product handles them as two separate flows.

Akış AFlow A

Değişiklik yönetişimiDatabase change governance

Şema veya veri değiştiren her betik.Every script that changes schema or data.

  • TalepRequest Betik, hedef sunucu ve bilet numarasıyla açılır.Opened with the script, target server and ticket number.
  • DoğrulamaValidation Betik gerçek dilbilgisiyle ayrıştırılır, kural kataloğundan etkin olanlar işletilir.The script is parsed with a real grammar and the enabled rules from the catalog are applied.
  • RiskRisk Tetiklenen kuralların en yükseği talebin bandını belirler.The highest tier among triggered rules sets the request band.
  • Politika ve onayPolicy and approval Sunucu, ortam ve banda göre onay adımları oluşur.Approval steps are generated from server, environment and band.
  • ÇalıştırmaExecution Onaydan sonra uygulama çalıştırır; isteğe bağlı zamanlama ve geri alma betiği.After approval the application executes it, with optional scheduling and a rollback script.
  • DenetimAudit Her adım imzalı denetim izine yazılır.Every step is written to a signed audit trail.
Akış BFlow B

Üretim sorgusu yönetişimiProduction query governance

Canlı ortamdan veri okuma talepleri.Requests to read data from the live environment.

  • Sorgu talebiQuery request Sorgu, gerekçesi ve teslim edilecek adreslerle açılır.Opened with the query, its justification and the delivery addresses.
  • Kural kontrolüRule check Kritik nesneye erişim ve sorgu kuralları işletilir.Critical object access and query rules are applied.
  • Hassas veri tespitiSensitive data detection Kolonlar desenlere ve doğrulayıcılara göre sınıflandırılır.Columns are classified against patterns and validators.
  • Maskeleme ve onayMasking and approval Hassas kolonlar maskelenir; maskesiz istenen kolon gerekçe ve ek onay ister.Sensitive columns are masked; an unmasked column needs a justification and an extra approval.
  • Kontrollü teslimControlled delivery Sonuç ekranda gösterilmez, parolalı şifreli paket olarak teslim edilir.The result is not shown on screen; it is delivered as an encrypted, password protected package.
  • DenetimAudit Kimin hangi veriyi hangi gerekçeyle aldığı kayıtta kalır.Who took which data and why stays on the record.
Yaşam döngüsüLifecycle

Bir talep baştan sona nasıl ilerlerHow a request moves from start to finish

Bir talep. Baştan sona izlenebilir bir yaşam döngüsü.One request. One lifecycle you can follow end to end.

1 TalepRequest Betikler, hedef sunucular ve bilet numarası girilir. Bilet biçimi kurumun kuralına göre doğrulanır. Scripts, target servers and the ticket number are entered. The ticket format is checked against your rule.
2 DoğrulamaValidation Betik veritabanı tipine uygun ayrıştırıcıyla çözümlenir. Sözdizimi hatası kaydı durdurur. The script is parsed with the grammar of its database type. A syntax error stops the save.
3 RiskRisk Band, tetiklenen kuralların en yükseğidir. Ortalama alınmaz, tek kritik bulgu bandı belirler. The band is the highest tier triggered. Nothing is averaged; one critical finding sets it.
4 PolitikaPolicy Sunucu, ortam ve talep tipine uyan politika seçilir, adımlar buna göre oluşur. The policy matching the server, environment and request type is selected and the steps follow from it.
5 OnayApproval Adımı gereken roldeki kişi kapatır. Kilitli adım rol üstünlüğüyle atlanamaz. The required role closes the step. A locked step cannot be skipped by seniority.
6 ÇalıştırmaExecution Uygulama betiği hedef sunucuda çalıştırır. Sonuç, süre ve hata mesajı kaydedilir. The application runs the script on the target server. Result, duration and any error are recorded.
7 DenetimAudit Her adım imzalı zincire yazılır ve tek dosyada kanıt olarak dışa aktarılabilir. Every step goes into a signed chain and can be exported as evidence in a single file.

Kural acele edildiğinde de işler. Asla atlanamaz işaretli bir kural tetiklendiğinde makine talebi kendi başına çalıştıramaz ve o kurala bağlı onay adımı atlanamaz. Kurulumda altı kural bu şekilde işaretlidir. The rule holds even under pressure. When a rule marked never skip is triggered, the machine cannot execute the request on its own and the approval step tied to that rule cannot be skipped. Six rules ship marked this way.

YeteneklerCapabilities

Ne yapar, neden önemliWhat it does, why it matters

CHANGE

Değişiklik yönetişimiChange governance

Ne yapar:What it does: Talep açma, çoklu betik, gerçek dilbilgisiyle ayrıştırma, risk bandı, kontrollü çalıştırma, zamanlanmış çalıştırma, geri alma betiği üretimi, izole sunucuda deneme ve sürüm paketi.Request creation, multiple scripts, real grammar parsing, risk banding, controlled execution, scheduled execution, rollback script generation, sandbox trial and release packages.

Neden önemli:Why it matters: Üretime giden betik, kimsenin masasında beklemeden aynı kapıdan geçer ve ne olduğu sonradan okunabilir.A script bound for production goes through the same gate every time, and what happened stays readable afterwards.

AyrıntıDetails
POLICY

Politika yönetişimiPolicy governance

Ne yapar:What it does: Sunucu, ortam ve talep tipine göre politika seçimi; kural anahtarı veya risk bandıyla tetiklenen adımlar; kritik nesne tanımları; atlanamaz adım kilidi; görevler ayrılığı parametreleri.Policy selection by server, environment and request type; steps triggered by rule key or risk band; critical object definitions; non skippable step locks; separation of duties parameters.

Neden önemli:Why it matters: Onay bir alışkanlık değil, yazılı bir kural haline gelir. Kuralın o günkü hali talebe dondurulur.Approval stops being a habit and becomes a written rule. The rule as it stood that day is frozen onto the request.

AyrıntıDetails
QUERY

Üretim sorgusu yönetişimiProduction query governance

Ne yapar:What it does: Sorgu talebi, hassas kolon tespiti, tam ve kısmi maskeleme, maskesiz kolon için gerekçeli ek onay, şifreli paket teslimi, alıcı adres onayı ve maskeleme denetim kaydı.Query requests, sensitive column detection, full and partial masking, justified extra approval for unmasked columns, encrypted package delivery, recipient address approval and a masking audit record.

Neden önemli:Why it matters: "Şu sorguyu çalıştır, sonucu bana at" cümlesi kayıt altına alınmış bir sürece dönüşür."Run this query and send me the result" turns into a recorded process.

AyrıntıDetails
AUDIT

Denetim ve kanıtAudit and evidence

Ne yapar:What it does: İmzalı denetim izi, ayrı veritabanında mühürlü ikinci kopya, veritabanı seviyesinde tetikleyici kaydı, talep bazlı kanıt dosyası, 31 hazır rapor ve nesne değişiklik geçmişi.A signed audit trail, a sealed second copy in a separate database, database level trigger records, a per request evidence file, 31 built in reports and object change history.

Neden önemli:Why it matters: Denetim hazırlığı bir projeye dönüşmez. Kanıt işin kendisinden üretilir.Audit preparation stops being a project. The evidence is produced by the work itself.

AyrıntıDetails
Ayıran dört şeyFour things that set it apart

Yığınınızda karşılığı olmayan dört şeyFour things your stack has no answer for

Yukarıdaki yeteneklerin bir kısmının kurumunuzda başka bir karşılığı zaten vardır. Aşağıdaki dördünün genellikle yoktur ve bu dördü, ürünün var olma sebebidir.Some of the capabilities above already have a counterpart in your organisation. These four usually do not, and they are the reason the product exists.

Boş rafThe empty shelf

Değişikliği değil, okumayı da yönetmekGoverning the read, not only the change

Değişiklik tarafında çoğu kurumun bir süreci vardır. Üretimden veri okuma tarafında neredeyse hiçbirinin yoktur. Bilet sistemi okuma taleplerini taşımaz, dağıtım hattı taşımaz, izleme aracı sorgunun çalıştığını görür ama gerekçesini ve dosyanın kime gittiğini görmez.On the change side most organisations have a process. On the side of reading production data, almost none do. Ticketing does not carry read requests, the pipeline does not carry them, and a monitor sees that the query ran but not why, nor where the file went.

Burada talep, gerekçe, hassas kolon tespiti, maskeleme, gerekçeli maskesiz onay, şifreli teslim ve onaylı alıcı adresi tek kayıtta durur. Kişisel veri denetiminde sorulan soruların tamamı buradan cevaplanır.Here the request, its reason, sensitive column detection, masking, a justified approval for unmasked columns, encrypted delivery and the approved recipient all sit on one record. Every question asked in a personal data audit is answered from it.

Sorgu yönetişimi →Query governance →
ZamanTime

Kararın kuralı o güne dondurulurThe rule behind a decision is frozen to its day

Kural setleri değişir. Altı ay önce verilmiş bir kararı bugünkü kuralla açıklamak yanıltıcıdır ve denetimde kabul edilmez. Talep açıldığında o gün yürürlükte olan kural seti kaydın üzerine dondurulur.Rule sets change. Explaining a decision from six months ago with today's rule is misleading and an auditor will not accept it. When a request opens, the rule set in force that day is frozen onto the record.

Bu, sonradan eklenebilecek bir özellik değil, veri modelinde baştan verilmesi gereken bir karardır. Sonradan eklemek geçmiş kayıtları kurtarmaz.This is not a feature that can be bolted on later; it is a decision the data model has to make from the start. Adding it afterwards does not rescue past records.

Denetim ve kanıt →Audit and evidence →
KanıtEvidence

Kanıt bizden bağımsız doğrulanır, istisna gizlenmezEvidence verifies without us, and exceptions are not hidden

Bir talebin tüm yaşam döngüsü mühürlü tek dosya olur. Mühür denetim kaydına yazılır; dosya sonradan verildiğinde özet yeniden hesaplanıp karşılaştırılır. "Kaydı tutan ekibe güvenin" cümlesine gerek kalmaz.A request's whole lifecycle becomes one sealed file. The seal is written into the audit record; hand the file back later and the digest is recomputed and compared. Nobody has to say "trust the team that keeps the record".

Ve dosya kendi aleyhine de yazar: talebi açan kişi kendi talebini çalıştırdıysa bu istisna olarak kayda geçer. Yönetişimin ölçüsü ihlalin hiç olmaması değil, olduğunda görünmesidir.And the file writes against itself: if the requester executed their own request, that is recorded as an exception. Governance is not measured by the absence of violations but by whether they surface.

Örnek dosyayı indirin →Download the sample file →
KapsamScope

Üç motor, tek model, gerçek dilbilgisiThree engines, one model, a real grammar

Kurumların çoğunda en az iki veritabanı motoru vardır ve bir motorun üreticisi diğerini yönetmez. Burada SQL Server, PostgreSQL ve Oracle aynı karar modeline girer; her biri kendi gerçek dilbilgisiyle çözümlenir.Most organisations run at least two database engines, and the maker of one does not govern the other. Here SQL Server, PostgreSQL and Oracle all enter the same decision model, each parsed with its own real grammar.

Gerçek dilbilgisi önemlidir: metin araması, yorum satırındaki bir silme ifadesi ile gerçeğini ayırt edemez. Kural ancak ifadenin sözdizim ağacı üzerinde çalıştığında güvenilirdir.The real grammar matters: text matching cannot tell a delete inside a comment from a real one. A rule is only reliable when it runs on the syntax tree of the statement.

Platform →Platform →

Kurum içinde kurulur, veriniz dışarı çıkmaz, arayüz ve destek Türkçedir ve uyum belgeleri KVKK diliyle yazılmıştır. Mevcut araçlarınızın nerede bittiğini ayrı bir sayfada karşılaştırıyoruz. It is installed inside your organisation, your data never leaves, and the interface and support are available in Turkish with compliance documents written in the language of local data protection law. We compare where your current tools end on a separate page.

Ürün ekranlarıProduct screens

Kararın ve kanıtın durduğu yerWhere the decision and the evidence live

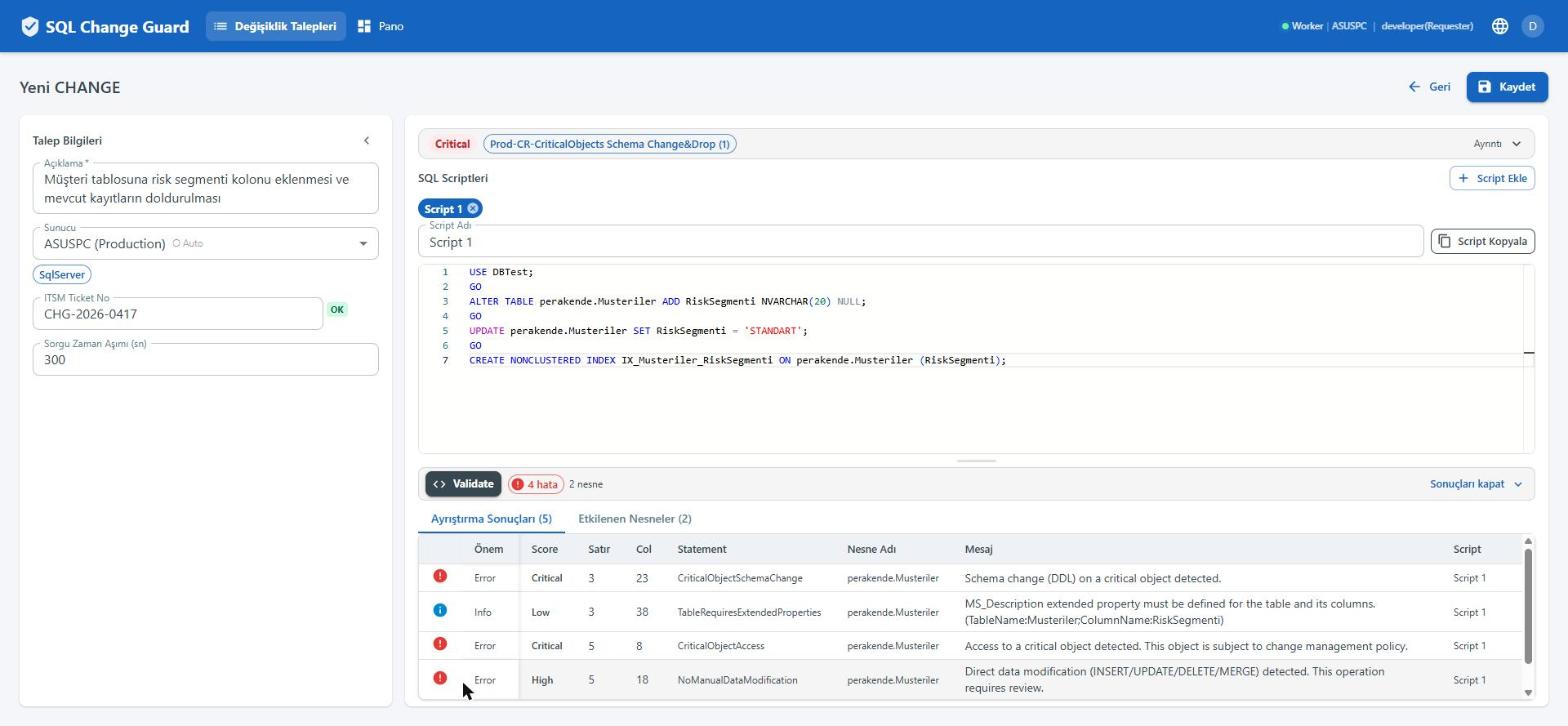
Değişiklik talebi ekranı: betik, doğrulama bulguları ve risk bandı
Değişiklik talebi ve riskChange request and risk Betik, tetiklenen kurallar ve talebin risk bandı aynı ekranda. The script, the rules it triggered and the request band, on one screen.
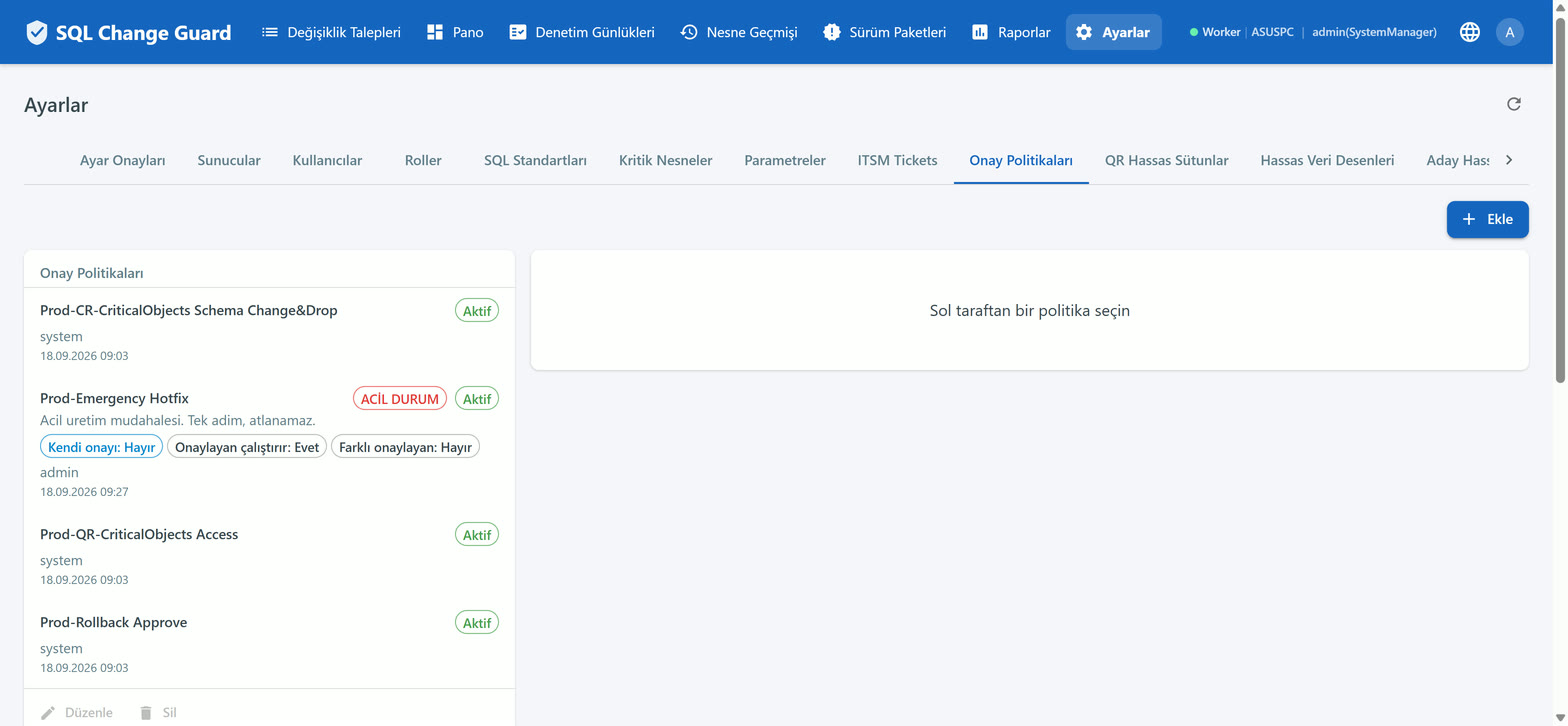
Onay politikası tanımlama ekranı: adımlar, roller ve tetikleme koşulları
Onay politikalarıApproval policies Hangi adımın ne zaman devreye gireceği burada yazılır. When each step comes into play is written here.
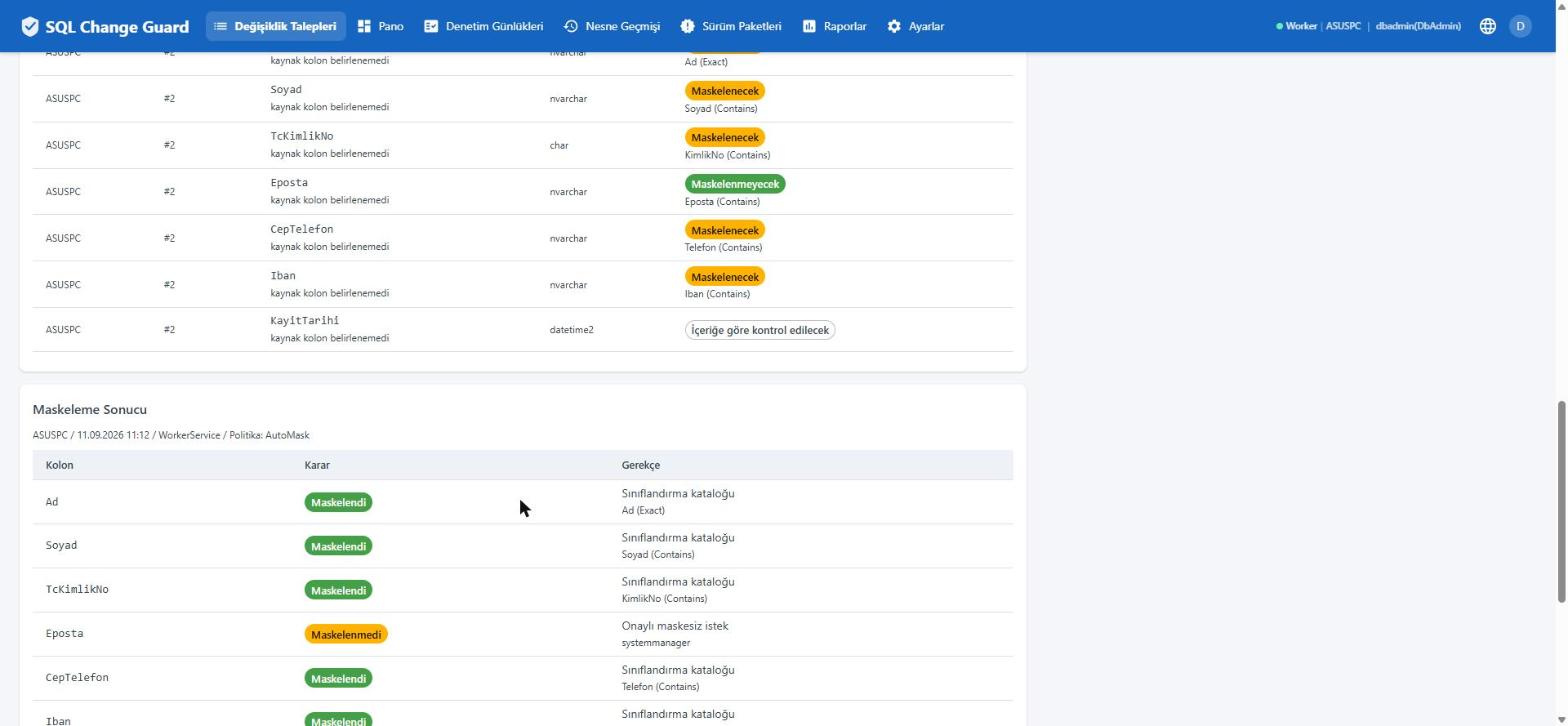
Sorgu sonucu talebi detayı: maskelenen kolonlar ve teslim bilgisi
Sorgu sonucu ve maskelemeQuery result and masking Hangi kolonun maskelendiği ve sonucun kime teslim edildiği. Which column was masked and who the result went to.
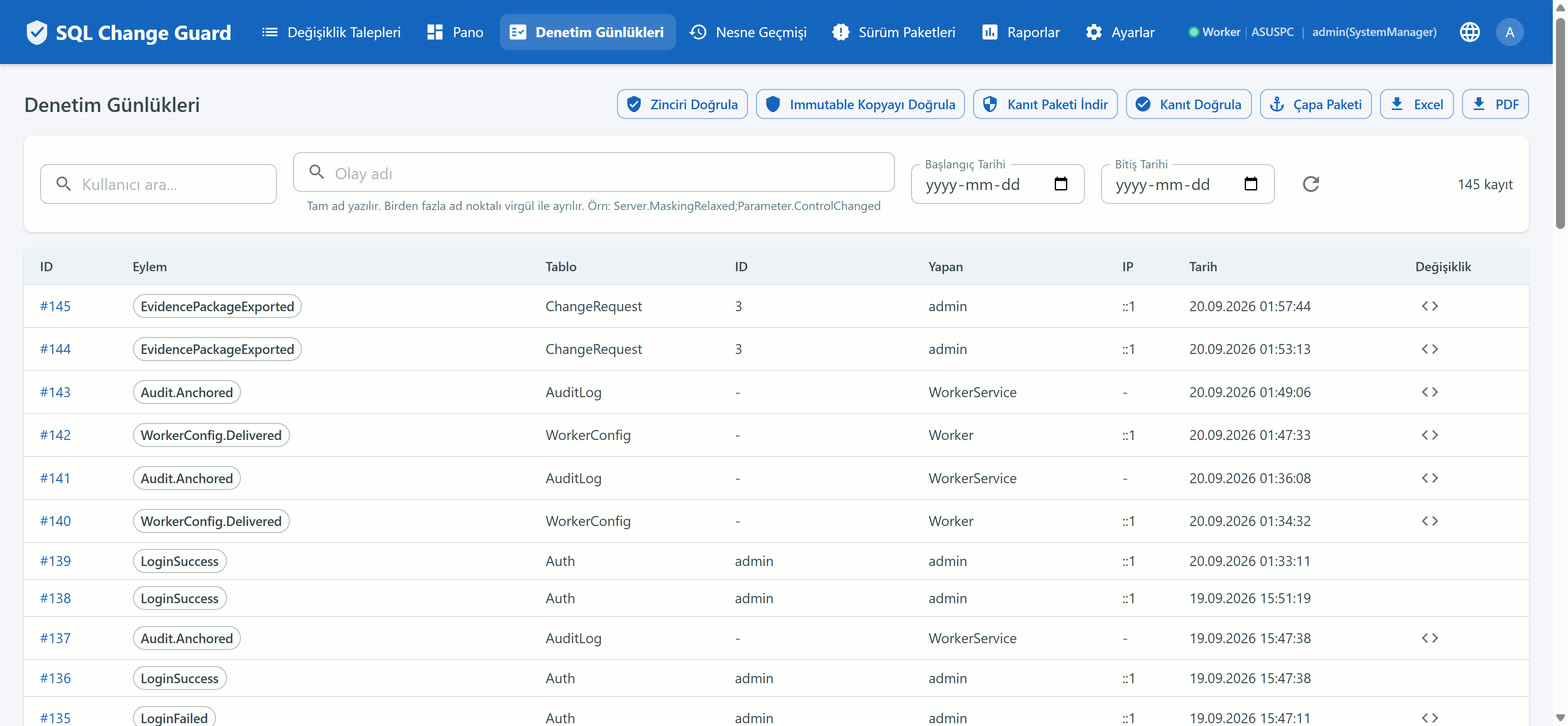
Denetim kayıtları ekranı: zincir doğrulama ve olay listesi
Denetim kayıtlarıAudit records Olay listesi ve zincirin bozulmadığını gösteren doğrulama. The event list and the check that shows the chain is unbroken.
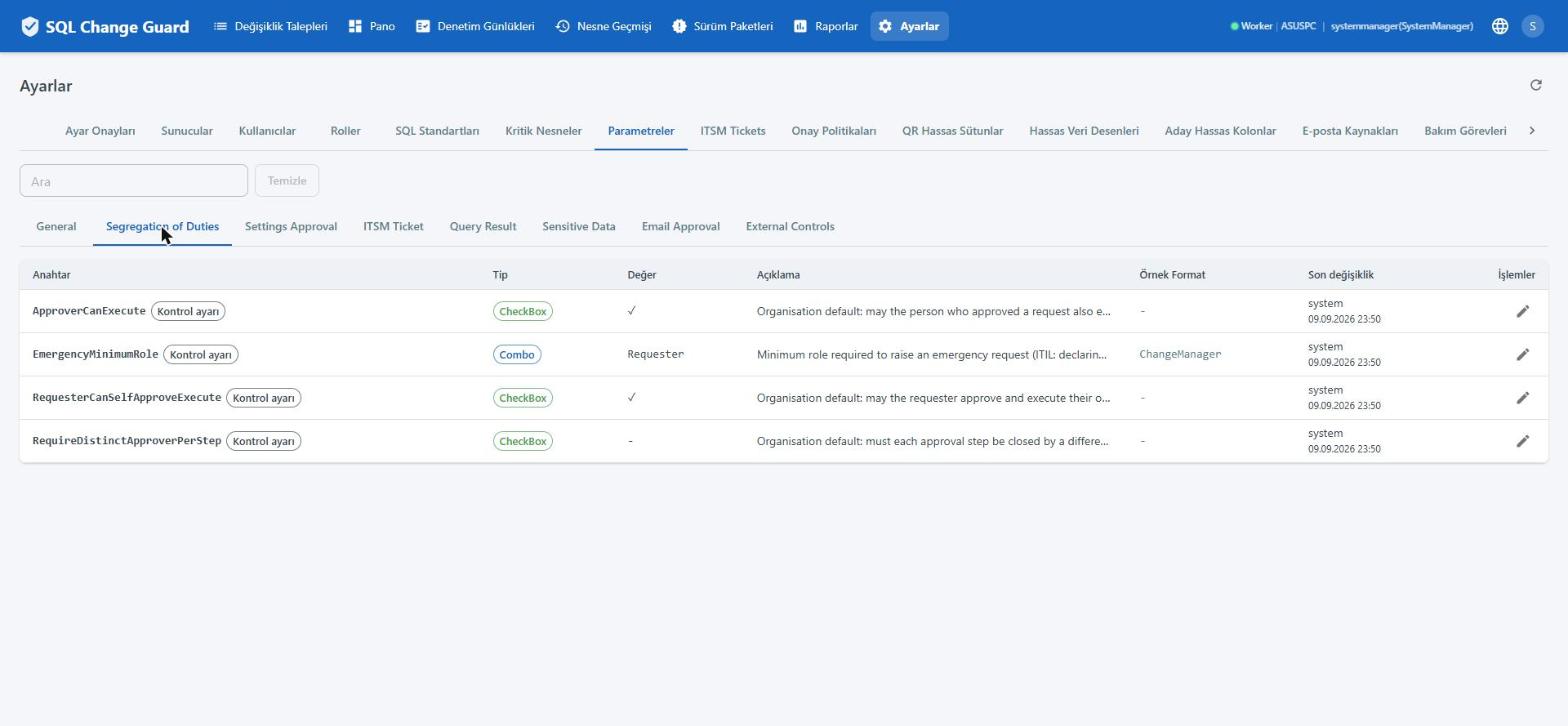
Parametreler ekranı, görevler ayrılığı sekmesi: onaylayan çalıştırabilir mi ve kendi talebini onaylayabilir mi ayarları
Görevler ayrılığı ayarlarıSegregation of duties settings Kimin neyi yapamayacağı bir belgede değil, burada yazılı. What nobody may do is written here rather than in a policy document.
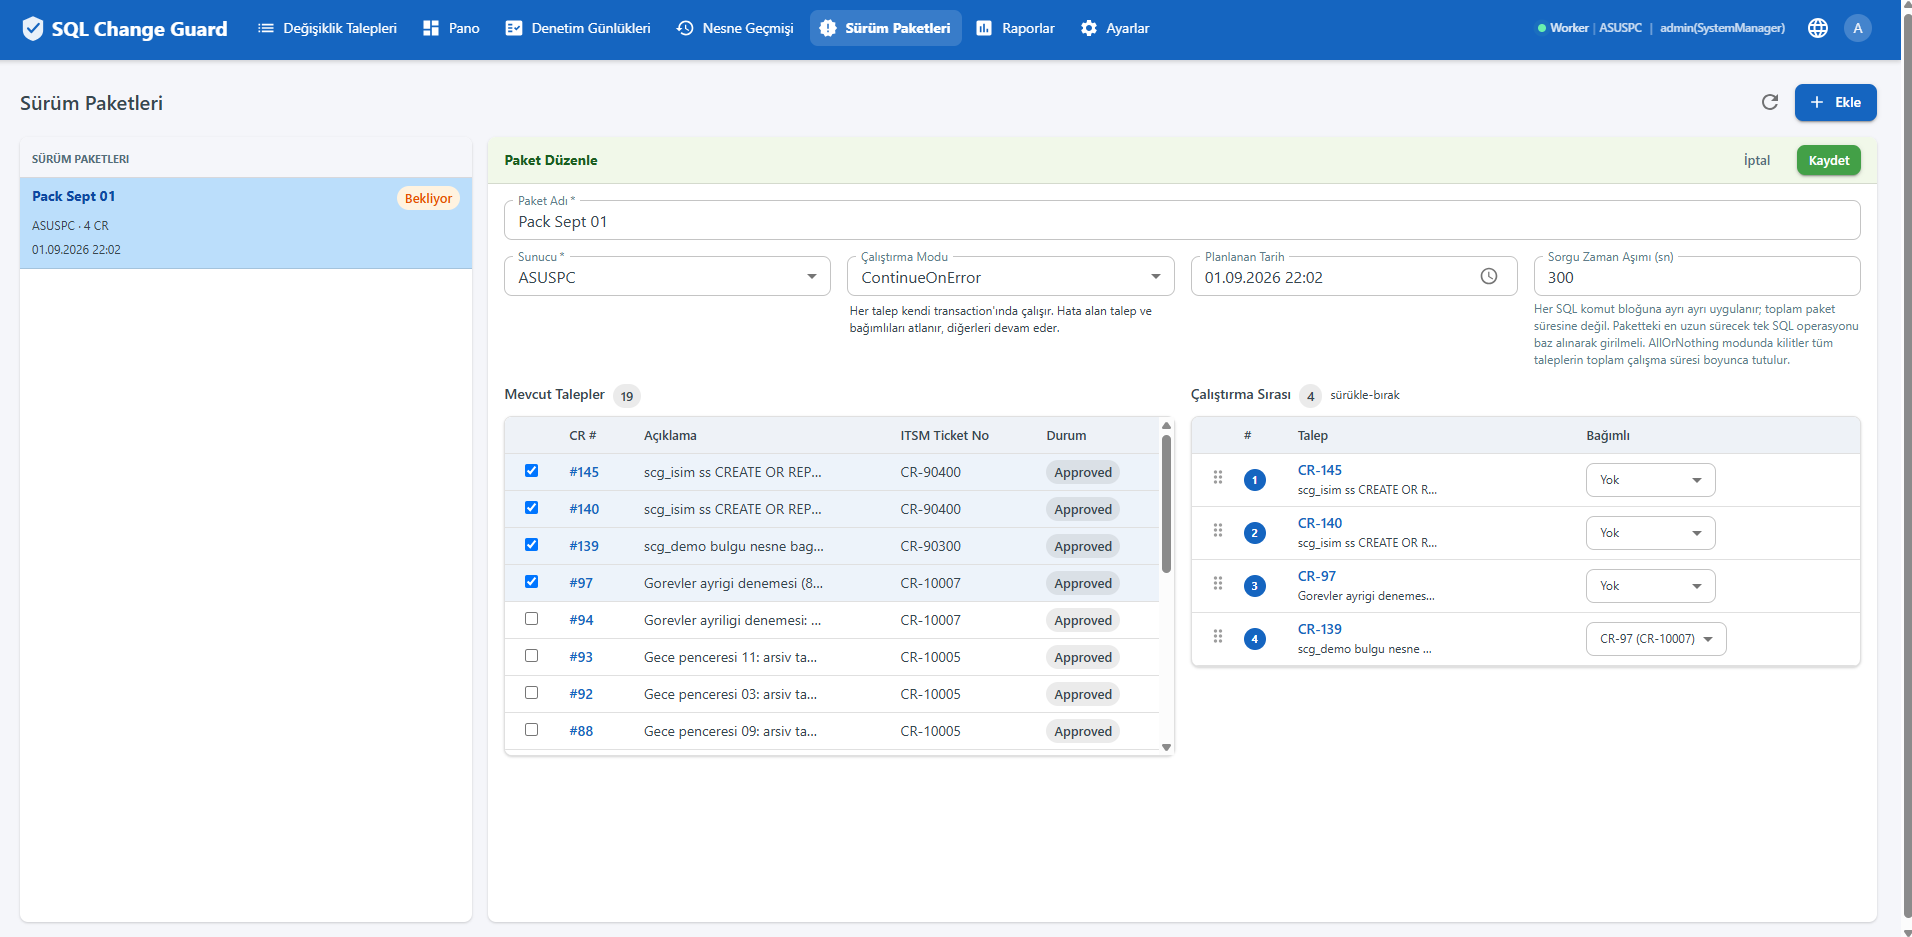
Sürüm paketleri ekranı: pakete alınan onaylı talepler, çalıştırma sırası ve bağımlılıklar
Sürüm paketleriRelease packages Onaylı talepler, çalıştırma sırası ve aralarındaki bağımlılık. Approved requests, the execution order and the dependencies between them.

Bu ekranların ürettiği şeyWhat these screens produce

Yukarıdakiler kararın verildiği yer. Kanıt ise bir ekran değil, bir dosya: bir talebin tüm yaşam döngüsü mühürlü tek dosya olarak dışa aktarılır ve denetçiye o dosya verilir. İçinde kim istedi, o gün hangi kural seti yürürlükteydi, zaman çizelgesi, betiğin parmak izi, risk gerekçesi, maskeleme kararı ve doğrulanmış denetim kayıtları vardır.The screens above are where the decision is made. The evidence is not a screen but a file: a request's whole lifecycle exports as one sealed file, and that file is what the auditor receives. It holds who asked, which rule set was in force that day, the timeline, the script fingerprint, the risk rationale, the masking decision and the verified audit records.

Ürünün gerçek çıktısıdır, tanıtım için hazırlanmış örnek değildir. Kayıt olmadan indirip inceleyebilirsiniz.It is real product output, not a mock-up made for a brochure. You can download and inspect it without signing up.

Ürün videolarıProduct videos

Çalışırken izleyinWatch it running

Slayt yok, ürünün kendisi. Üç sütun için üç akış: üretime giden bir değişiklik, denetçinin eline geçen kanıt ve üretimden çıkan veri.No slides, the product itself. Three flows for the three pillars: a change going to production, the evidence the auditor receives and data leaving production.

Uçtan uca gösterimEnd to end walkthrough

Bir değişiklik üretime nasıl giderHow a change reaches production

Bir kolon ekleme talebi, açıldığı andan üretimde göründüğü ana kadar. Bir buçuk dakika, sessiz, anlatım ekrandaki metinle. Videodaki her ekran ürünün gerçek çıktısıdır.A request to add a column, from the moment it is opened to the moment it appears in production. A minute and a half, silent, narrated by on-screen text. Every screen in it is real product output.

  • Betik çözümlenir, risk bandı hesaplanırThe script is parsed and the risk band is computed
  • Kural, kaydetmeden önce durdururA rule stops the work before it is even saved
  • Onay yolu talebin içeriğine göre kurulurThe approval path is built from the content of the request
  • Onaylayan kişide çalıştırma düğmesi kapalıdırFor the approver, the execute button stays closed

Denetçinin eline ne geçiyorWhat the auditor actually receives

Kanıt denetim için ayrıca hazırlanmaz, işin kendisinden çıkar ve ürün olmadan da doğrulanır.Evidence is not prepared separately for the audit. It comes out of the work itself and can be verified without the product.

Üretimden veri nasıl çıkarHow data leaves production

Değişiklik çoğu kurumda kontrol edilir, okuma edilmez. Bu akış okuma tarafını gösterir.Most organisations govern changes but not reads. This flow follows the read side.

MimariArchitecture

Ortamınızın neresinde dururWhere it sits in your environment

Kendi sunucunuzda çalışır. Veritabanlarınıza giden yol üzerinde durur, verinizi dışarı taşımaz.It runs on your own servers. It sits on the path to your databases and moves no data outside.

Kullanıcılar ve rollerUsers and roles Web arayüzü. Kurumsal dizin ve ikinci faktör ile giriş. Sekiz rol seviyesi. Web interface. Sign in with the corporate directory and a second factor. Eight role levels.
SQL Change Guard Uygulama sunucusu ve arka plan servisi. Kayıtlarını kendi veritabanında tutar. Application server and background service. It keeps its records in its own database.
RiskRiskKural motoruRule engine
PolitikaPolicyAdım kararıStep decision
OnayApprovalRol ve kilitRole and lock
Hedef veritabanlarıTarget databases SQL Server, PostgreSQL, Oracle. Her biri kendi dilbilgisiyle çözümlenir ve çalıştırılır. SQL Server, PostgreSQL, Oracle. Each is parsed and executed with its own grammar.
Denetim ve kanıtAudit and evidence İmzalı iz, ayrı veritabanında mühürlü kopya ve veritabanı seviyesinde tetikleyici kaydı. A signed trail, a sealed copy in a separate database and database level trigger records.

Bilet sisteminiz, hattınız ve log platformunuz yerinde kalır. Ürün bunların yerine geçmez. Your ticketing system, your pipeline and your log platform stay where they are. The product does not replace them.

Kurulum ve güvenlikDeployment and security

Kurumunuzun soracağı dört soruThe four questions your organisation will ask

Verimiz nereye gidiyor?Where does our data go?

Hiçbir yere. Ürün kendi sunucunuzda çalışır ve kayıtlarını kendi veritabanınızda tutar. Bulut bağımlılığı yoktur, üretim veriniz kurum dışına çıkmaz.Nowhere. The product runs on your own servers and keeps its records in your own database. There is no cloud dependency and your production data does not leave the organisation.

Veritabanımıza ne yetki veriyoruz?What permissions does it need?

Şema, ürünle gelen numaralı betiklerle kurulur. Banka ve benzeri kurumlar için doğrulama modu vardır: betikleri veritabanı yöneticiniz kendi süreçlerinden geçirerek uygular ve uygulamanın hesabına şema değiştirme yetkisi verilmez.The schema is installed from numbered scripts shipped with the product. There is a validation mode for banks and similar institutions: your database administrator applies the scripts through their own process and the application account is never granted schema modification rights.

Kimlik doğrulama nasıl?How does sign in work?

Kurumsal dizin ile giriş desteklenir, ikinci faktör açılabilir. Yetki sekiz rol seviyesi ve ekran bazlı izinlerle yönetilir. Yetki kontrolü ekranda değil sunucuda uygulanır.Sign in through your corporate directory is supported and a second factor can be enabled. Authorisation is managed through eight role levels and screen level permissions, and it is enforced on the server rather than in the interface.

KVKK tarafında ne kazandırır?What does it give us for data protection?

Üretim verisine erişim talebe bağlanır, hassas kolonlar maskelenir ve maskesiz erişim gerekçesiyle kayıt altına alınır. Kullanıcı parolaları ve sunucu parolaları şifreli saklanır, denetim izi imzalanır. Uyumluluk dokümanı indirilebilir.Access to production data is tied to a request, sensitive columns are masked, and unmasked access is recorded with its justification. User and server passwords are stored encrypted and the audit trail is signed. A compliance document is available to download.

KanıtEvidence

Denetçiye ne gösterirsinizWhat you show the auditor

Bir talebin tüm yaşam döngüsü tek bir dosya olarak dışa aktarılır: kim istedi, o gün hangi kural seti yürürlükteydi, zaman çizelgesi, betiğin parmak izi, risk gerekçesi, maskeleme kararı ve doğrulanmış denetim kayıtları.

A request's whole lifecycle exports as a single file: who asked, which rule set was in force that day, the timeline, the script fingerprint, the risk rationale, the masking decision and the verified audit records.

Dosyanın kendi mührü vardır ve mühür denetim kaydına yazılır. Dosyanın üretimden sonra değişmediği bu mühürle kontrol edilir.

The file carries its own seal, and the seal is written into the audit record. That seal is how you check the file has not changed since it was produced.

İstisnalar gizlenmez. Talebi açan kişi kendi talebini çalıştırdıysa dosya bunu istisna olarak yazar. Yönetişimin ölçüsü ihlalin hiç olmaması değil, olduğunda görünmesidir.

Exceptions are not hidden. If the requester executed their own request, the file records it as an exception. Governance is not measured by the absence of violations but by whether they surface.

Anlatmıyoruz, gösteriyoruzWe are not describing it, we are showing it

Aşağıdaki dosyalar ürünün gerçek çıktısıdır, tanıtım için hazırlanmış örnek değildir. Kayıt olmadan, e-posta vermeden indirip inceleyebilirsiniz. Denetim veya uyum tarafındaysanız kararınızı bir sunumdan değil, bu dosyadan verin.The files below are real product output, not mock-ups made for a brochure. Download and inspect them without signing up or leaving an email. If you sit on the audit or compliance side, judge us on this file rather than on a slide deck.

PDF

Örnek denetim dosyasıSample evidence dossier

Tek bir talebin tüm yaşam döngüsü: talep, o günkü kural seti, zaman çizelgesi, betiğin parmak izi, risk gerekçesi, onaylar ve denetim kayıtları.One request's whole lifecycle: the request, the rule set of that day, the timeline, the script fingerprint, the risk rationale, the approvals and the audit records.

Dossier.pdf indirinDownload Dossier.pdf
JSON

Makine okunur hali ve mühürMachine readable copy and seal

Aynı dosyanın veri hali ve paket özeti. Mühür denetim izine yazılır; dosya sonradan ürüne verildiğinde özet yeniden hesaplanır ve karşılaştırılır.The same file as data, plus the package digest. The seal is written into the audit trail; hand the file back to the product later and the digest is recomputed and compared.

Dossier.json · · Manifest.json
PDF

KVKK uyumluluk belgesiData protection compliance note

Kişisel veri, saklama, maskeleme ve denetim izi konularında ürünün ne yaptığı ve neyi yapmadığı. Hukuk ve uyum biriminin soracağı sorular için.What the product does and does not do about personal data, retention, masking and the audit trail. Written for the questions your legal and compliance team will ask.

Uyumluluk_KVKK_TR.pdf indirin Download Compliance_KVKK_EN.pdf
PDF

Sistem mimarisi ve topolojiSystem architecture and topology

Bileşenler, ağ topolojisi, veri akışı ve hangi hesabın neye eriştiği. Güvenlik incelemesine girmeden önce okunacak belge.Components, network topology, data flow and which account reaches what. The document to read before a security review starts.

SistemMimarisi_TR.pdf indirin Download SystemArchitecture_EN.pdf
Kim ne kazanırWho benefits

Rolünüze göre ne değişirWhat changes for your role

CIO, IT Director

Veritabanı operasyonlarının ne kadar kontrollü olduğunu ve geçmişte ne olduğunu tek yerden görürsünüz.You see from one place how controlled database operations are and what happened in the past.

CISO, Compliance

Üretim verisine kimin, hangi gerekçeyle eriştiği ve hangi kolonun maskesiz gittiği kayıtta durur.Who reached production data, for what stated reason, and which column went out unmasked, all stay on record.

Veritabanı ekibiDatabase team

Talep, onay ve çalıştırma tek akışta ilerler. Geri alma betiği ve izole denemeyi ürün üretir.Request, approval and execution move in one flow. The rollback script and the sandbox trial come from the product.

CTO, DevOps Manager

Veritabanı işleri kontrollü bir teslim sürecinin içine girer, hattınız yerinde kalır.Database work joins a controlled delivery process while your pipeline stays where it is.

İç DenetimInternal Audit

Kim ne yaptı, neden yaptı, kim onayladı ve ne çalıştırıldı sorularının kanıtı tek dosyada.Who did what, why, who approved it and what ran: the evidence sits in one file.

Change Manager

Onay kuralı yazılı hale gelir ve talebin o günkü kural seti sonradan da okunabilir.The approval rule becomes written, and the rule set of that day stays readable later.

Infrastructure Manager

Hangi sunucuda ne çalıştığı, kimin yetkisi olduğu ve bekleyen işin nerede durduğu görünür olur.What ran on which server, who holds which permission and where pending work stands all become visible.

Yeni bir araç değil, eksik olan katmanNot another tool. The layer that was missing.

Hattınız kalır. Biletiniz kalır. Kaydınız kalır. Yönetişim eklenir.Your pipeline stays. Your ticket stays. Your log stays. Governance is added.

Database Operations Governance
Şema sürümlemeSchema versioning
Hat ve otomasyonPipeline and automation
Değişiklik biletiChange ticketing
Sunucu izlemeServer monitoring
Log ve SIEMLog and SIEM
YedeklemeBackup

Kurumların çoğu yeni bir araç almak istemiyor. Haklılar, zaten yeterince araç var.

Most enterprises do not want another tool. They are right. There are already enough tools.

Bu ürün var olanların üstüne sorumluluk koyar. Hattınız çalışmaya devam eder, değişiklik biletiniz yerinde kalır, log platformunuz aynı kalır. Değişen tek şey şudur: bunların hepsi artık tek bir karar ve kanıt modeline bağlanır.

This product places accountability above the ones you have. Your pipeline keeps running, your change ticket stays where it is, your log platform does not move. One thing changes: all of them now report into a single decision and evidence model.

Ne yapmadığını da söyleyelim: betiğinizi yazmaz, testinizi koşmaz, biletinizi kapatmaz. Bir tek şey yapar ve onu hiçbir aracınız yapmıyor: üretime giden işin kararını, kuralını ve kanıtını aynı kayıtta tutar.

It is also worth saying what it does not do. It does not write your scripts, it does not run your tests and it does not close your ticket. It does one thing, and none of your tools is doing it: it keeps the decision, the rule and the evidence of work bound for production on the same record.

Yeni bir araç eklemiyorsunuz. Sahip olduklarınızın üstüne tek bir karar ve kanıt modeli koyuyorsunuz.You are not adding another tool. You are putting one decision and evidence model on top of what you already run.

Kısa cevaplarShort answers

İlk görüşmelerde en sık gelen altı soru. Uzun hali sık sorulan sorular sayfasında.The six questions that come up most in a first conversation. The longer answers are on the frequently asked questions page.

Database Operations Governance nedir?What is Database Operations Governance?

Üretim veritabanına dokunan işin, gerçekleşmeden önce yazılı bir kurala göre değerlendirilmesi, yetkili bir kişi tarafından onaylanması ve sonradan kanıtlanabilmesidir. İki alanı birden kapsar: veritabanı değişikliği ve üretim verisine erişim. Değişiklik yönetiminden farkı, işin nasıl taşınacağını değil, geçmesine izin verilip verilmeyeceğini düzenlemesidir.It is the practice of assessing work that touches a production database against a written rule before it happens, having an authorised person approve it, and being able to prove it afterwards. It covers two areas at once: database change and production data access. It differs from change management in that it governs whether the work is allowed through rather than how it is carried.

SQL Change Guard tam olarak ne yapar?What exactly does SQL Change Guard do?

Bir betiği gerçek dilbilgisiyle ayrıştırır, kural kataloğuna göre bulgularını çıkarır ve bir risk bandı belirler. Politikanın gerektirdiği onaylar tamamlanmadan çalıştırma açılmaz. Çalıştırma anında metnin özeti alınıp denetim kaydına mühürlenir, sonuç ve etkilenen satır sayısı kaydedilir. Nesne tanımı değişiklikleri için geri alma betiği önceden hazırlanır. Üretimden veri çekme talepleri de aynı döngüden geçer: hassas kolonlar maskelenir, sonuç şifreli paketle teslim edilir.It parses a script with a real grammar, produces findings against a rule catalog and sets a risk band. Execution does not open until the approvals the policy requires are complete. At execution the digest of the text is sealed into the audit record, and the outcome and affected row count are recorded. For object definition changes a rollback script is prepared in advance. Requests to extract production data go through the same loop: sensitive columns are masked and the result is delivered as an encrypted package.

Jira, ServiceNow veya dağıtım hattımızın yerine mi geçiyor?Does it replace Jira, ServiceNow or our delivery pipeline?

Hayır. Bilet sistemi ne istendiğini, dağıtım hattı ne taşındığını, izleme aracı ne çalıştığını bilir. Hiçbiri çalışan metnin onaylanan metin olduğunu gösteremez, çünkü bu bilgi hiçbirinin görev tanımında yoktur. SQL Change Guard o bağı kurar ve bilet numarasıyla mevcut sisteminize bağlanır. Mevcut araçlarla ilişkisi.No. A ticketing system knows what was asked for, a pipeline knows what it carried, a monitor knows what ran. None of them can show that the text that ran is the text that was approved, because that is outside all of their remits. SQL Change Guard makes that link and connects to your existing system by ticket number. How it relates to your current tools.

Hangi veritabanlarını destekliyor?Which databases are supported?

Yönetilen hedef sistem olarak SQL Server, PostgreSQL ve Oracle. Her biri kendi dilbilgisiyle ayrıştırılır; ortak bir sözdizimi varsayımı yapılmaz. Ürünün kendi kayıtları bugün SQL Server üzerinde tutulur.As managed targets, SQL Server, PostgreSQL and Oracle. Each is parsed with its own grammar; no shared syntax is assumed. The product keeps its own records on SQL Server today.

Nerede çalışır, verimiz dışarı çıkar mı?Where does it run, and does our data leave?

Kurumun kendi ağında çalışır; bulut hizmeti değildir. Betikleriniz ve sorgu sonuçlarınız hiçbir dış servise gönderilmez, ürünün kayıtları da sizin sunucunuzda durur. Şifreleme anahtarları sizin yapılandırmanızdadır; üründe gömülü anahtar yoktur. Güvenlik mimarisi.It runs inside your own network; it is not a cloud service. Your scripts and query results are never sent to any external service, and the product keeps its records on your server. Encryption keys live in your configuration; there is no key embedded in the product. Security architecture.

Süreci yavaşlatır mı?Will it slow us down?

Yavaşlatan şey kontrol değil, her değişikliğe aynı ağırlıkta kontrol uygulamaktır. Onay derinliği risk bandına göre belirlenir: düşük bant tek onayla geçer, yüksek bant çok kişili onay ister. Ölçülmesi gereken sayı onay adımı sayısı değil, talebin açılışından çalıştırılmasına kadar geçen süredir.What slows things down is not control, it is applying the same weight of control to every change. Approval depth follows the risk band: a low band passes with one approval, a high band requires several. The number to measure is not how many approval steps exist but how long a request takes from opening to execution.

Kurumunuzda bu katman var mıDoes this layer exist in your organisation

Altı soru. Beş dakika. Satış görüşmesi değil.Six questions. Five minutes. Not a sales call.

1Üretimde çalışan bir değişikliğin hangi kurala göre onaylandığını, o günün kuralıyla birlikte gösterebiliyor musunuz?Can you show under which rule a change running in production was approved, together with the rule as it stood that day?
2Üretim verisini kimin, hangi gerekçeyle okuduğunu tek bir yerden görebiliyor musunuz?Can you see in one place who read production data and for what stated reason?
3Acil durumda atlanan adımlar, gerekçesiyle birlikte kayıtta duruyor mu?Are the steps skipped during an emergency recorded with their justification?
4Denetim kanıtınızı, kaydı tutan kişiden bağımsız olarak doğrulayabiliyor musunuz?Can your audit evidence be verified independently of whoever keeps the records?
5Üretim veritabanına değişiklik ulaştıran kaç ayrı yol var ve kaçı aynı yönetişim modelinin içinde?How many separate paths deliver change to your production database, and how many sit inside the same governance model?
6En kıdemli veritabanı yöneticiniz bir ay izne çıksa, sürüm sırası nerede yazılı?If your most senior database administrator took a month of leave, where is the release order written down?
Bu sorulardan üçüne "evet" diyemiyorsanız sorun aracınızda değil. Kurumda o katman yok.If you cannot say yes to three of these, the problem is not your tooling. The layer is missing.