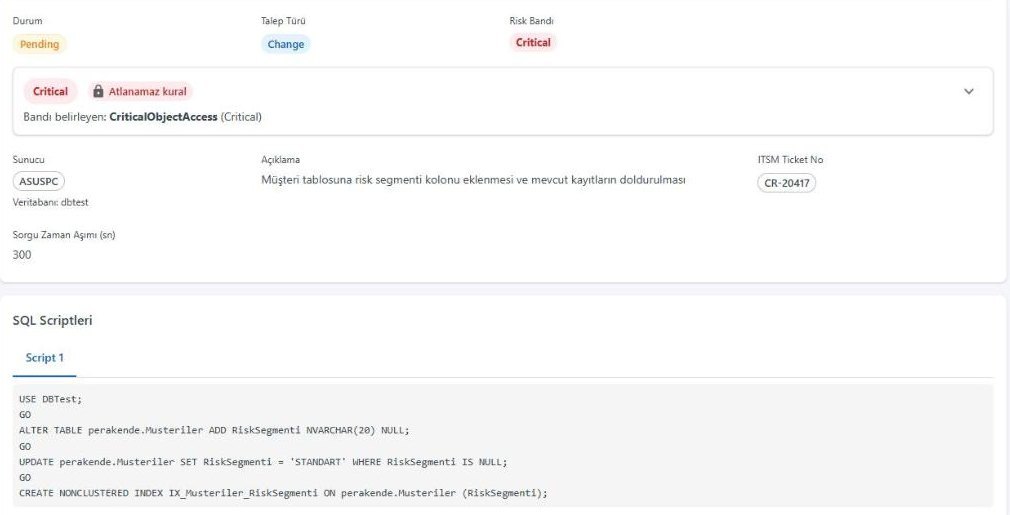
Risk bandı: en kötü bulgu belirlerRisk band: the worst finding decides
Atlanamaz kural: onay adımı kilitlenirNon skippable rule: the approval step is locked
Bilet numarası bilet sisteminde doğrulanırThe ticket number is checked in your ticketing system
Betiğin parmak izi kayda yazılırThe script fingerprint goes on the record
Çoğu kurumda bu sorunun cevabı tek bir sistemde durmaz. Her araç zincirin bir halkasını bilir; yürütme anındaki bağ hiçbirinin görev tanımında değildir.In most organisations the answer does not sit in any one system. Each tool knows one link of the chain; the link at the moment of execution is in none of their remits.
Neyin istendiğini ve kimin onay verdiğini bilir. Üretimde çalışacak betiğin son halini bilmez.Knows what was asked for and who signed it off. It does not know the final text of the script that will run in production.
Taşıdığı değişikliği bilir. Gece yapılan acil müdahale gibi hattın dışından giden işi görmez.Knows the change it carried. It does not see work that goes outside the pipeline, such as an emergency fix at night.
Neyin çalıştığını görür. Hangi onaya ve hangi gerekçeye dayandığını bilmez.Sees what ran. It does not know which approval and which justification it rests on.
Denetçi "bu değişikliği kim onayladı, çalışan metin onaylanan metin miydi" diye sorduğunda cevap, birkaç sistemin kaydı elle eşleştirilerek kurulur. Üretim verisinin okunması ise çoğu kurumda hiç bir talebe bağlı değildir. When an auditor asks who approved this change and whether the text that ran was the text that was approved, the answer is pieced together by matching records across several systems by hand. Reading production data, in most organisations, is not tied to any request at all.
| AraçTool | GöreviIts job | SQL Change Guard ne eklerWhat SQL Change Guard adds |
|---|---|---|
| Jira, ServiceNow | Talebi ve iş onayını tutarHolds the request and the business approval | Bilet numarasını kayıtta ve çalıştırma anında bilet sisteminde sorgular, olayları bilete not olarak yazar. Bağlantı isteğe bağlıdır.Checks the ticket number in the ticketing system at save time and again at execution, and writes events back as notes. The connection is optional. |
| CI/CD, Liquibase, FlywayCI/CD, Liquibase, Flyway | Şema değişikliğini sürümler ve taşırVersions and ships schema change | Hattın dışından giden betikler ve üretim verisi talepleri için politika, onay ve kanıt. Bugün dağıtım hatlarıyla doğrudan bağlantısı yoktur.Policy, approval and evidence for scripts that go outside the pipeline and for production data requests. There is no direct connection to delivery pipelines today. |
| DAM ve SIEMDAM and SIEM | Veritabanı etkinliğini izler, olayları toplarMonitors database activity and collects events | Çalışan işi onaya ve gerekçeye bağlar; denetim olaylarını syslog, CEF, LEEF veya JSON ile SIEM'e gönderir. Canlı trafiği dinlemez.Links the work that ran to its approval and justification, and sends audit events to your SIEM over syslog, CEF, LEEF or JSON. It does not listen to live traffic. |
| Veritabanı araçlarıDatabase tools | Doğrudan erişim (SSMS, DBeaver, SQL Developer)Direct access (SSMS, DBeaver, SQL Developer) | Bu yolları kapatmaz. Kontrol, ürünün kapısından geçen işe uygulanır; doğrudan erişim yetkisini kurum kendi yetki modeliyle daraltır.It does not close these paths. Control applies to work that goes through the product; your organisation narrows direct access with its own permission model. |
Betik, veritabanı tipine uygun ayrıştırıcıyla çözümlenir ve kural kataloğuna göre değerlendirilir. Risk bandı tetiklenen en yüksek bulguya eşittir. Sunucu, ortam ve banda göre onay adımları oluşur; atlanamaz işaretli bir kurala bağlı adım rol kıdemiyle geçilemez. O gün yürürlükte olan kural seti talebin üzerine dondurulur.The script is parsed with the grammar of its database type and assessed against the rule catalog. The risk band equals the highest finding triggered. Approval steps follow from server, environment and band; a step tied to a rule marked non skippable cannot be passed by seniority. The rule set in force that day is frozen onto the request.
Değişiklik yönetişimi →Change governance →Onaylanan içeriğin parmak izi kayda yazılır ve çalıştırmadan önce yeniden karşılaştırılır; içerik sonradan değiştiyse çalıştırma durur ve bu olay kayda geçer. Sonuç, süre, hata ve etkilenen satır sayısı kaydedilir. Hedefte işlenip işlenmediği belirsiz kalan bir çalıştırma sessizce başarılı sayılmaz, uzlaştırmaya alınır.The fingerprint of the approved content goes on the record and is compared again before execution; if the content changed afterwards, execution stops and that event is recorded. Outcome, duration, errors and affected row counts are recorded. A run whose commit on the target is uncertain is not quietly counted as a success; it goes to reconciliation.
Hedef veritabanı ayrıntıları →Target database details →Her talep için denetim dosyası (PDF ve JSON) üretilir: kim istedi, hangi kural geçerliydi, kim onayladı, ne çalıştı, hangi istisnalar oluştu. İmza anahtarı tanımlı kurulumda paket imzalanır ve içindeki betikle ürüne bağlanmadan doğrulanır. Denetim kaydı SQL Server ledger tablosunda yalnız ekleme yapılarak tutulur; imzalı defter özetleri veritabanı dışında saklanabilir.An evidence file (PDF and JSON) is produced per request: who asked, which rule applied, who approved, what ran and which exceptions occurred. Where a signing key is configured the package is signed, and it verifies with the script inside it without connecting to the product. The audit record is kept append only in a SQL Server ledger table; signed ledger digests can be stored outside the database.
Örnek denetim dosyası (PDF) →Sample evidence file (PDF) →Veri talebi gerekçesiyle açılır. Hassas kolonlar tespit edilip maskelenir; maskesiz istenen kolon gerekçe ve ek onay ister. Sonuç ekranda gösterilmez, parolalı şifreli paketle onaylı alıcıya teslim edilir ve kimin indirdiği kayda geçer.A data request opens with its justification. Sensitive columns are detected and masked; a column requested unmasked needs a justification and an extra approval. The result is not shown on screen; it is delivered to the approved recipient in a password protected encrypted package, and who downloaded it is recorded.
Sorgu yönetişimi →Query governance →Sınırı açıkça söyleyelim. Ürün kendi kapısından geçen işi yönetir ve kanıtlar. Uygulama veritabanına tam yönetici erişimi olan birine karşı mutlak koruma sağlamaz; amaç yetkisiz değişikliği zorlaştırmak ve bağımsız noktalardan fark edilir kılmaktır. Kanıt nasıl doğrulanır Let us state the limit plainly. The product governs and evidences the work that goes through it. It does not give absolute protection against someone with full administrator access to the application database; the aim is to make unauthorised change harder and to make it detectable from independent points. How evidence is verified
Web uygulaması IIS üzerinde, arka plan servisi Windows servisi olarak çalışır. Kayıtlar sizin SQL Server veritabanınızda durur. Bulut hizmeti değildir; lisans çevrimdışı doğrulanır.The web application runs on IIS and the background service as a Windows service. Records stay in your own SQL Server database. It is not a cloud service; the licence is verified offline.
Hedef veritabanlarına uygulama sunucusundan standart sürücüyle bağlanılır. Hedef sunucuya yazılım yüklenmez; gereken yetki, ürünün o hedefte yapacağı işle sınırlı bir hesaptır.Target databases are reached from the application server through standard drivers. Nothing is installed on the target server; the permission needed is an account limited to the work the product will do there.
Kurum hesabıyla (OpenID Connect, SAML) veya LDAP ile girişte parola ürüne kaydedilmez; yerel kullanıcı parolası BCrypt ile özetlenir. Hedef bağlantı parolaları AES-256-GCM ile şifreli saklanır. Anahtarlar sizin yapılandırmanızda durur.With corporate sign in (OpenID Connect, SAML) or LDAP the password is not stored by the product; local user passwords are hashed with BCrypt. Target connection passwords are stored encrypted with AES-256-GCM. The keys live in your configuration.
Yalnız sizin açtığınız ve adresini sizin verdiğiniz bağlantılar: e-posta, bilet sistemi, kimlik sağlayıcı, SIEM. Zaman damgası açıksa dışarıya yalnız dosya özeti gider; tek ayarla kapatılır.Only connections you switch on, to addresses you provide: email, ticketing, identity provider, SIEM. If timestamping is on, only a file digest goes out; one setting turns it off.
Tek bir sunucu, küçük bir ekip, kendi ağınızda. Pilotun sonunda elinizde kendi ortamınızdan üretilmiş denetim dosyaları olur; kararınızı bir sunumdan değil o dosyalardan verirsiniz.One server, a small team, inside your own network. At the end of the pilot you hold evidence files produced from your own environment, and you decide on those files rather than on a slide deck.