EkranlarScreens
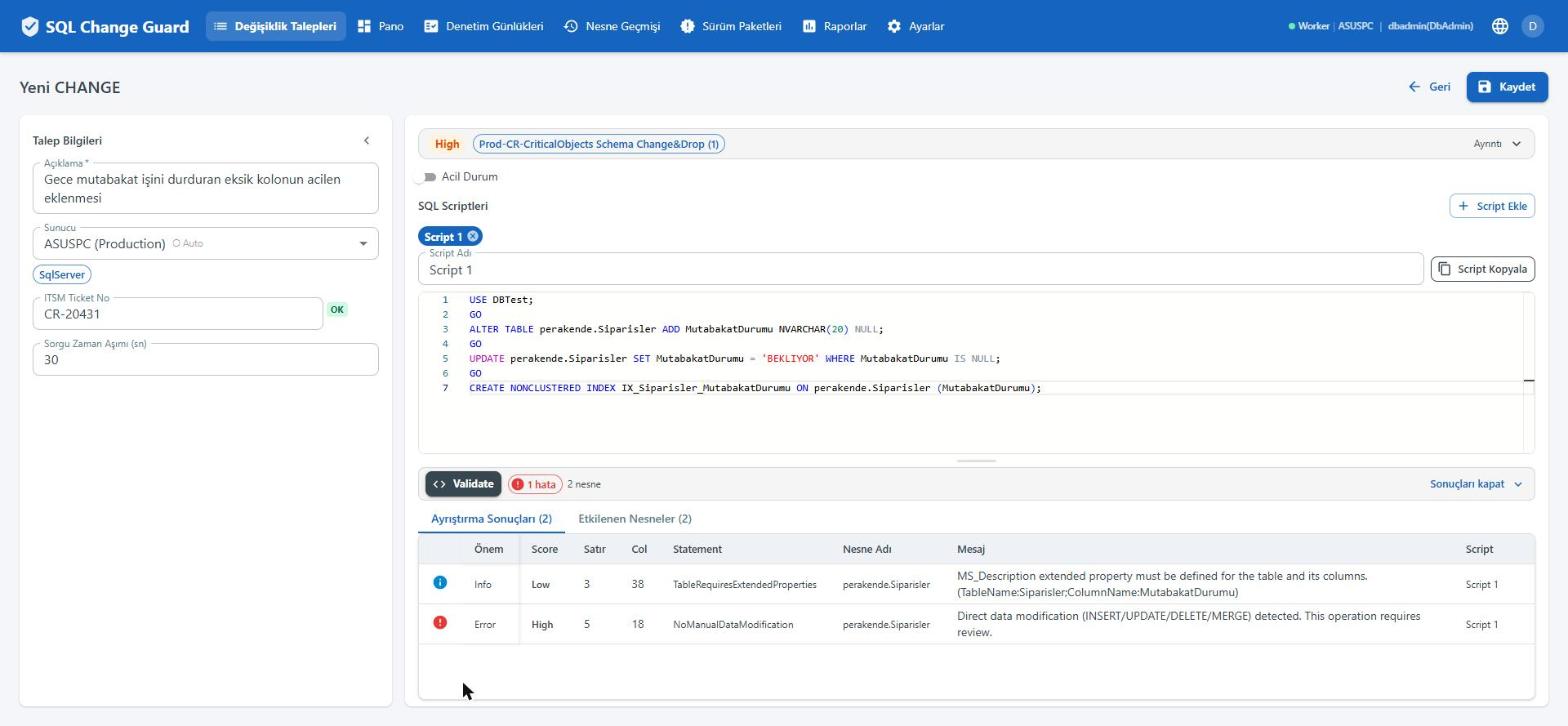
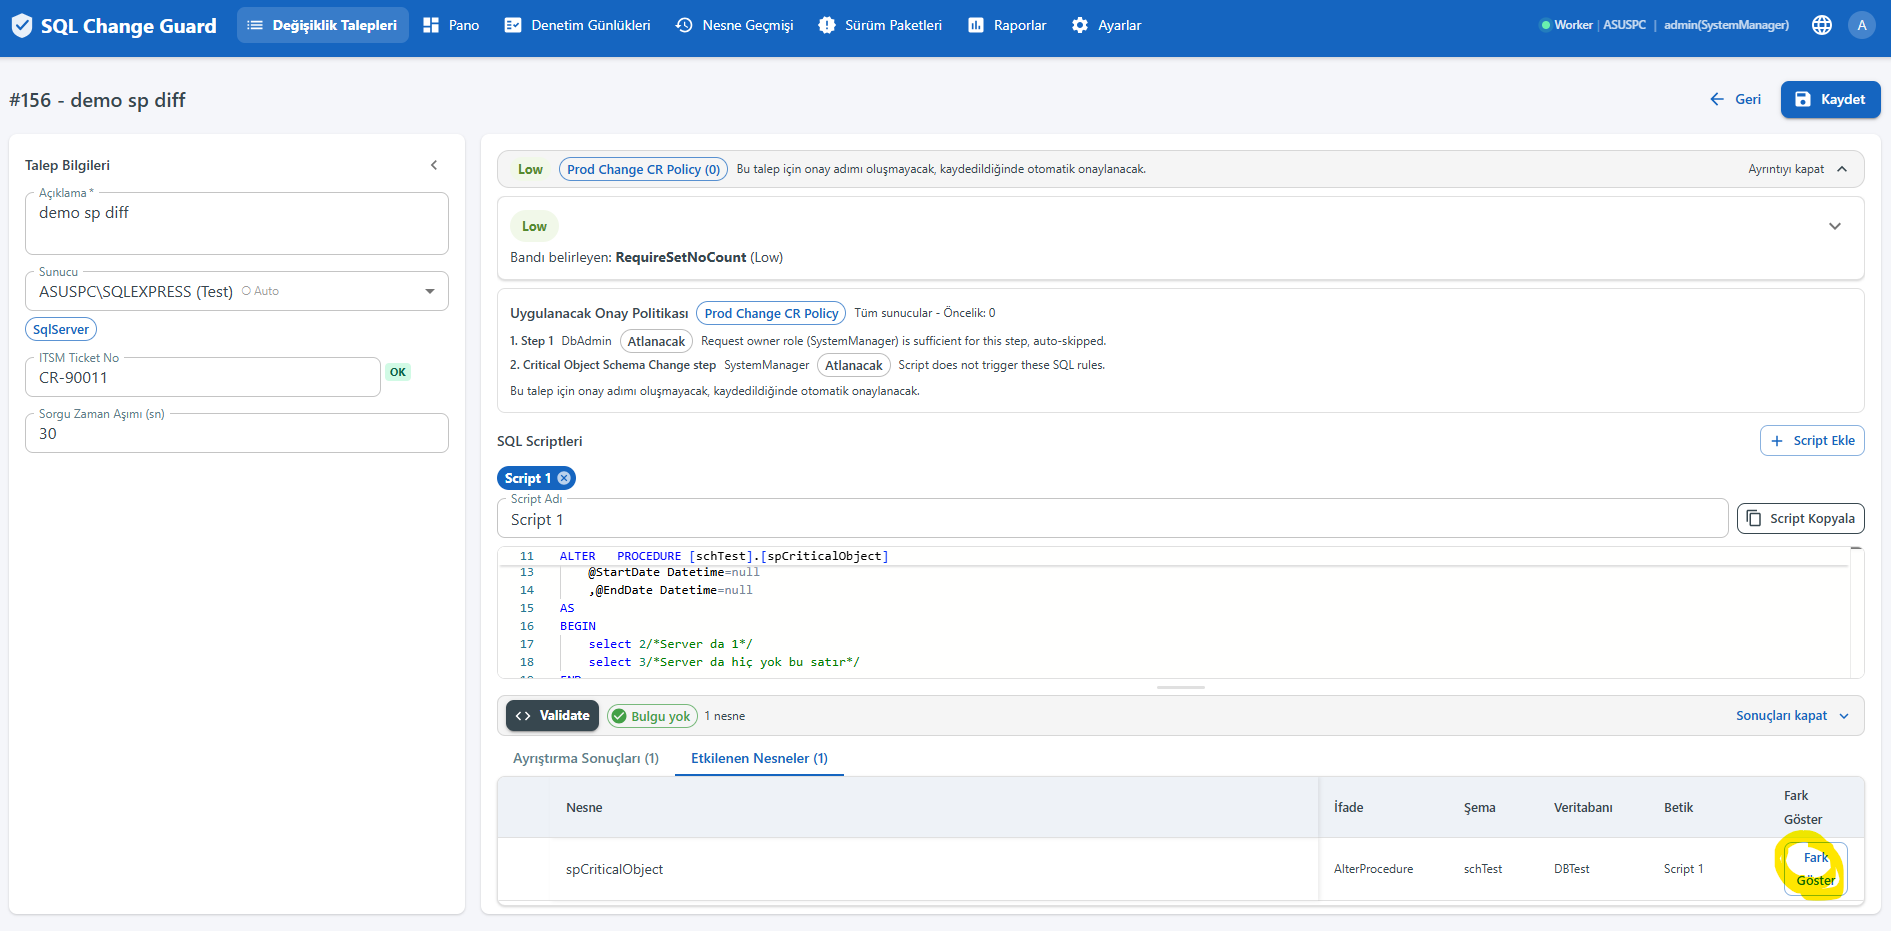
Ürün üzerinden üretime giden her betik aynı kapıdan geçer: doğrulama, risk bandı, politika, onay, çalıştırma ve denetim. Ürün veritabanına başka yoldan bağlanmayı engellemez; bunun için kişisel üretim yetkilerinin kaldırılması ve izleme kayıtlarıyla eşleştirme gerekir. Karar kuralı yazılıdır, kanıt işin kendisinden çıkar. Every script sent to production through the product goes through the same gate: validation, risk band, policy, approval, execution and audit. The product does not block other routes into the database; that takes removing personal production rights and matching against monitoring records. The decision rule is written down and the evidence comes out of the work itself.
Değişiklik yönetimi bir değişikliğin nasıl planlanacağını, taşınacağını ve yayına alınacağını düzenler. Sorusu şudur: bu iş üretime nasıl gider? Bilet sistemleri, dağıtım hatları ve şema göç araçları bu soruyu cevaplar.Change management organises how a change is planned, carried and released. Its question is how the work gets to production. Ticketing systems, delivery pipelines and schema migration tools answer that question.
Değişiklik yönetişimi ise o işin geçmesine izin verilip verilmeyeceğini ve geçtiğinin nasıl kanıtlanacağını düzenler. Sorusu şudur: bu iş hangi kurala göre değerlendirildi, kim izin verdi ve çalışan metnin onaylanan metin olduğunu neye dayanarak söylüyoruz? Üç bileşeni vardır ve üçü de yazılı olmak zorundadır: kural, kapı ve kanıt.Change governance organises whether the work is allowed through and how you prove that it was. Its question is which rule assessed the work, who allowed it, and on what basis you claim the text that ran is the text that was approved. It has three components and all three must be written down: the rule, the gate and the evidence.
İki disiplin birbirinin alternatifi değildir. SQL Change Guard yönetim araçlarınızın yerine geçmez; onların cevaplamadığı ikinci soruyu cevaplar. Veritabanı değişikliği ile üretim verisine erişimi tek çatı altında ele alan bu yaklaşımı Database Operations Governance olarak adlandırıyoruz.The two disciplines are not alternatives. SQL Change Guard does not replace your management tools; it answers the second question they leave open. We call the approach that brings database change and production data access under one roof Database Operations Governance.
Üç ayrı fren vardır ve üçü farklı sertliktedir.There are three brakes and they are not equally hard.
Betik ayrıştırılamıyorsa talep hiçbir koşulda kaydedilmez. Bu fren kapatılamaz.If the script cannot be parsed, the request is never saved. This brake cannot be turned off.
Kural setinde "kaydı engeller" işaretli bir standart tetiklenirse kayıt oluşmaz. Kurulumda yedi kural bu şekilde işaretlidir; örneğin WHERE içermeyen UPDATE ve DELETE, betik içinde elle transaction açma ya da kapatma.If a standard marked "blocks save" is triggered, no record is created. Seven rules ship with this flag, for example UPDATE and DELETE without WHERE, and opening or closing a transaction by hand inside the script.
Yüksek dereceli diğer bulgularda kullanıcıya "riskleri gördüm" onayı gösterilir ve talep ancak ikinci gönderimde kaydedilir.For other high tier findings the user is shown an acknowledgement, and the request is only saved on the second submission.
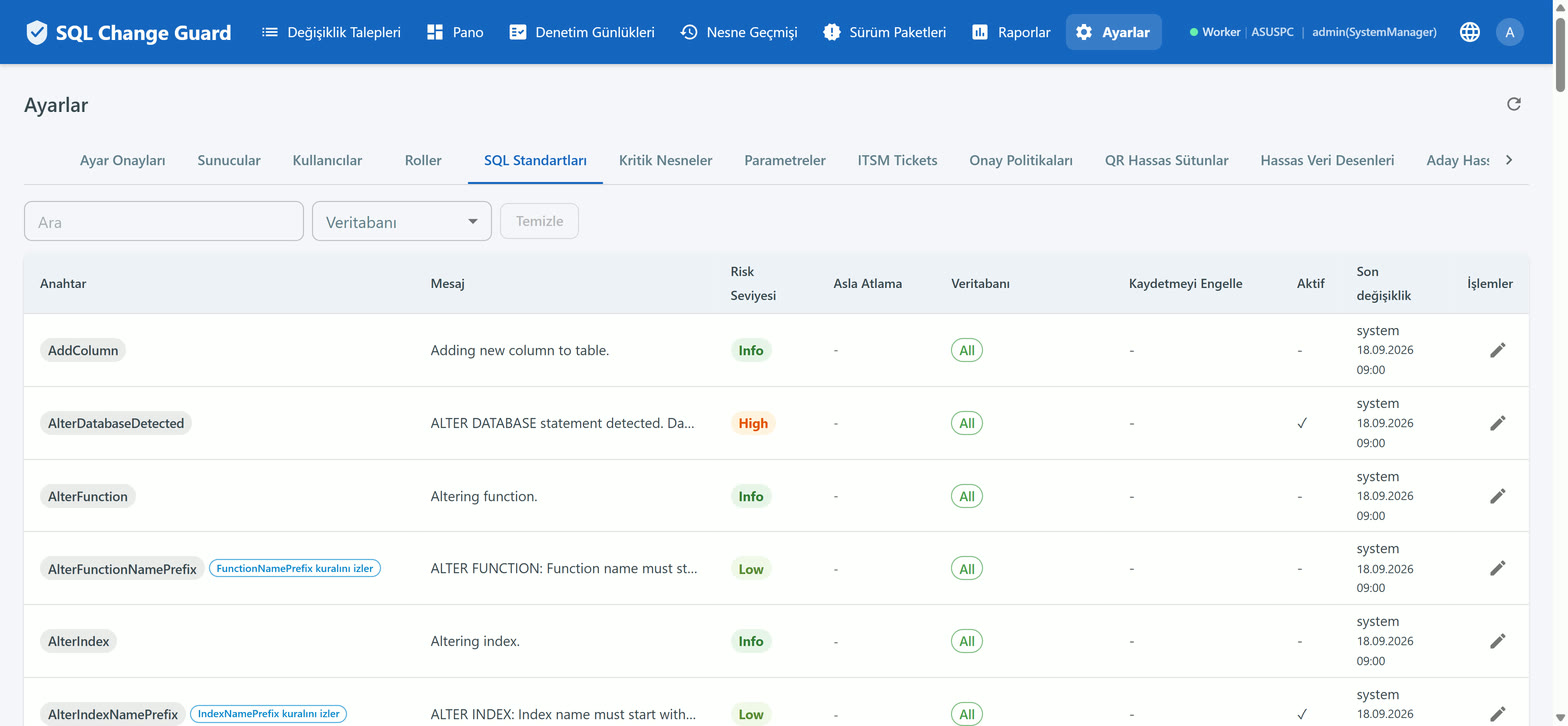
Kural seti kurumun elindedir. Kurulumla seksen sekiz maddelik bir SQL standardı kataloğu gelir. Her biri açılıp kapatılabilir, önem derecesi değiştirilebilir ve hangi veritabanı tiplerinde geçerli olduğu belirlenebilir. Ekran: Ayarlar, SQL Standartları. The rule set belongs to you. A catalogue of eighty eight SQL standards ships with the product. Each can be switched on or off, its tier changed, and the database types it applies to selected. Screen: Settings, SQL Standards.
Her SQL standardı beş dereceden birini taşır: Info, Low, Medium, High, Critical. Bir talebin bandı, o talepte tetiklenen kuralların en yüksek derecesidir.
Every SQL standard carries one of five tiers: Info, Low, Medium, High, Critical. A request's band is the highest tier among the rules it triggered.
Ortalama alınmaz ve puanlar toplanmaz. Bunun sebebi basittir: elli küçük bulgunun ortalaması, tek bir kritik bulguyu gizler. En kötü durum yaklaşımı bu gizlenmeyi engeller.
Nothing is averaged and no points are summed. The reason is simple: the average of fifty small findings hides a single critical one. A worst case approach prevents that.
Ekranda ayrıca 0 ile 100 arasında bir sayı görürsünüz. Bu sayı bandın okunur karşılığıdır ve hiçbir kapı kararında kullanılmaz. Karar bandın ve kural bayraklarının işidir.
The screen also shows a number between 0 and 100. That number is a readable projection of the band and is used in no gate decision. Decisions belong to the band and the rule flags.
Asla atlanamaz kurallar. Sekiz kural kurulumda bu işaretle gelir: kritik nesne silme, kritik nesneye erişim, kritik nesnede şema değişikliği, işletim sistemi komutu çalıştırma, yetki değişikliği, bağlı sunucu kullanımı ve betik içinde elle COMMIT ya da ROLLBACK yazılması. Biri tetiklendiğinde makine talebi kendi başına çalıştıramaz ve o kurala bağlı onay adımı atlanamaz. Rules that can never be skipped. Eight rules ship with this flag: dropping a critical object, accessing a critical object, schema change on a critical object, running an operating system command, permission changes, linked server usage and a manual COMMIT or ROLLBACK written inside the script. When one is triggered, the machine cannot execute the request on its own and the approval step tied to that rule cannot be skipped.
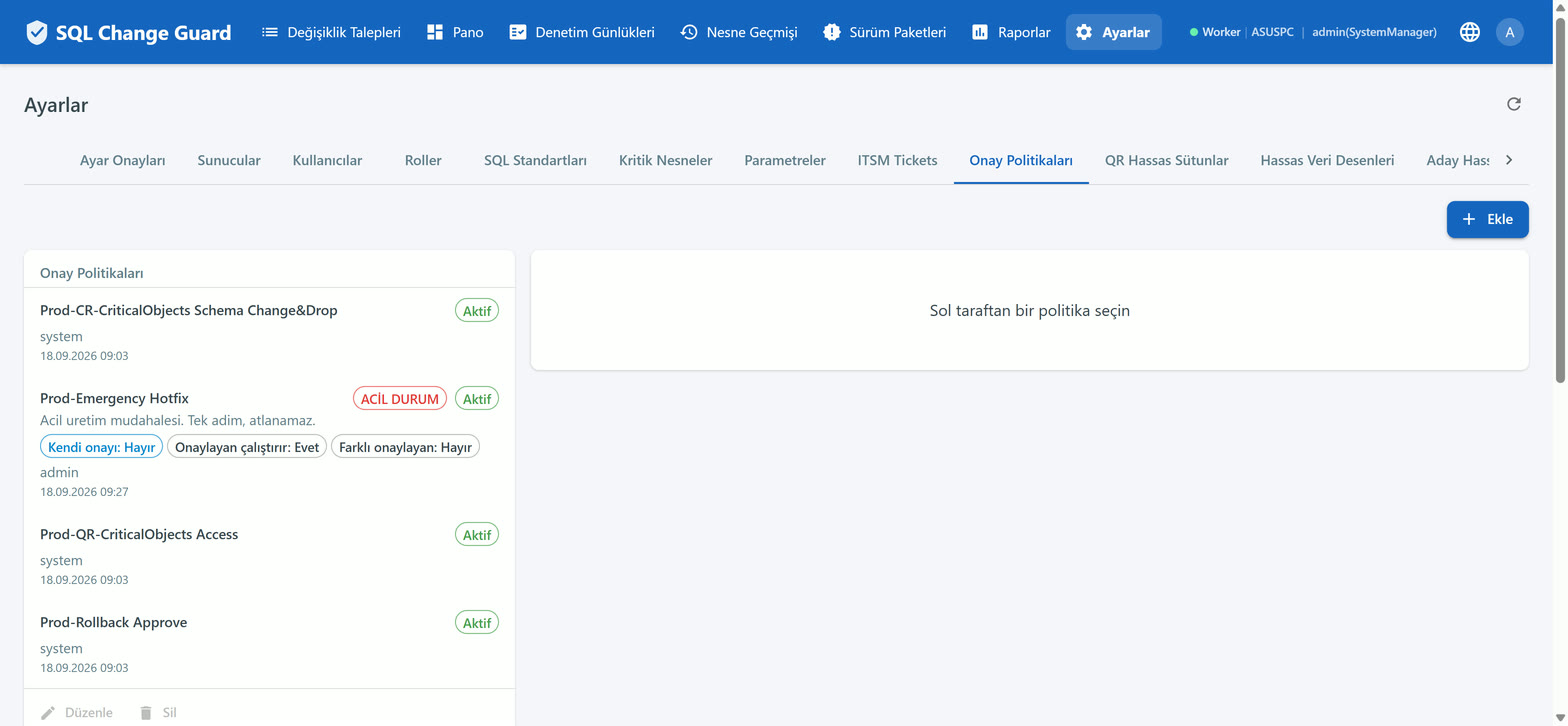
Onay bir alışkanlık değil, yazılı bir kuraldır. Kural talep kaydedilirken talebe dondurulur.Approval is not a habit. It is a written rule, and it is frozen onto the request at save time.
Aday politika şu özgüllük sırasıyla aranır: belirli sunucu, sonra ortam, sonra genel. Aynı kademede birden çok aday varsa öncelik değeri karar verir. Çok sunuculu sorgu talebinde her sunucu için ayrı çözüm yapılır ve en çok onay adımı üreten politika kazanır.Candidate policies are searched in this order of specificity: a specific server, then the environment, then global. When several candidates sit at the same level, the priority value decides. On a multi server query request each server is resolved separately and the policy that produces the most approval steps wins.
Onaylayan rol; belirli kural anahtarlarıyla tetikleme; risk bandı eşiğiyle tetikleme; düşük bantta atlama; talep sahibinin rolü yeterliyse atlama; ve adımı her koşulda bekleten kilit.The approver role; triggering on specific rule keys; triggering at a risk band threshold; skipping at a low band; skipping when the requester's own role is high enough; and a lock that makes the step wait under all conditions.
En sık karıştırılan nokta. Bir adımı koşullu yapan yalnız iki alan vardır: kural anahtarı ve bant eşiği. Koşullu bir adım tetiklendiğinde, talebi açan kişinin rolü onaylayan rolünü karşılıyor diye ya da bant düşük diye atlanmaz; yalnız adıma açıkça yazılmış rol atlaması işleyebilir, adım kilitliyse o da işlemez. Buna karşılık koşulsuz bir taban adım, kendi talebini onaylama ayarı açıkken, talebi açan kişinin rolü onaylayan rolüne eşit veya üstündeyse atlanır. The point most often misread. Only two fields make a step conditional: the rule key and the band threshold. Once a conditional step is triggered it is not skipped because the requester's role meets the approver role, nor because the band is low; only a role skip written explicitly on the step can apply, and not even that if the step is locked. A plain base step, by contrast, is skipped when the requester's own role is at or above the approver role, provided self approval is allowed.
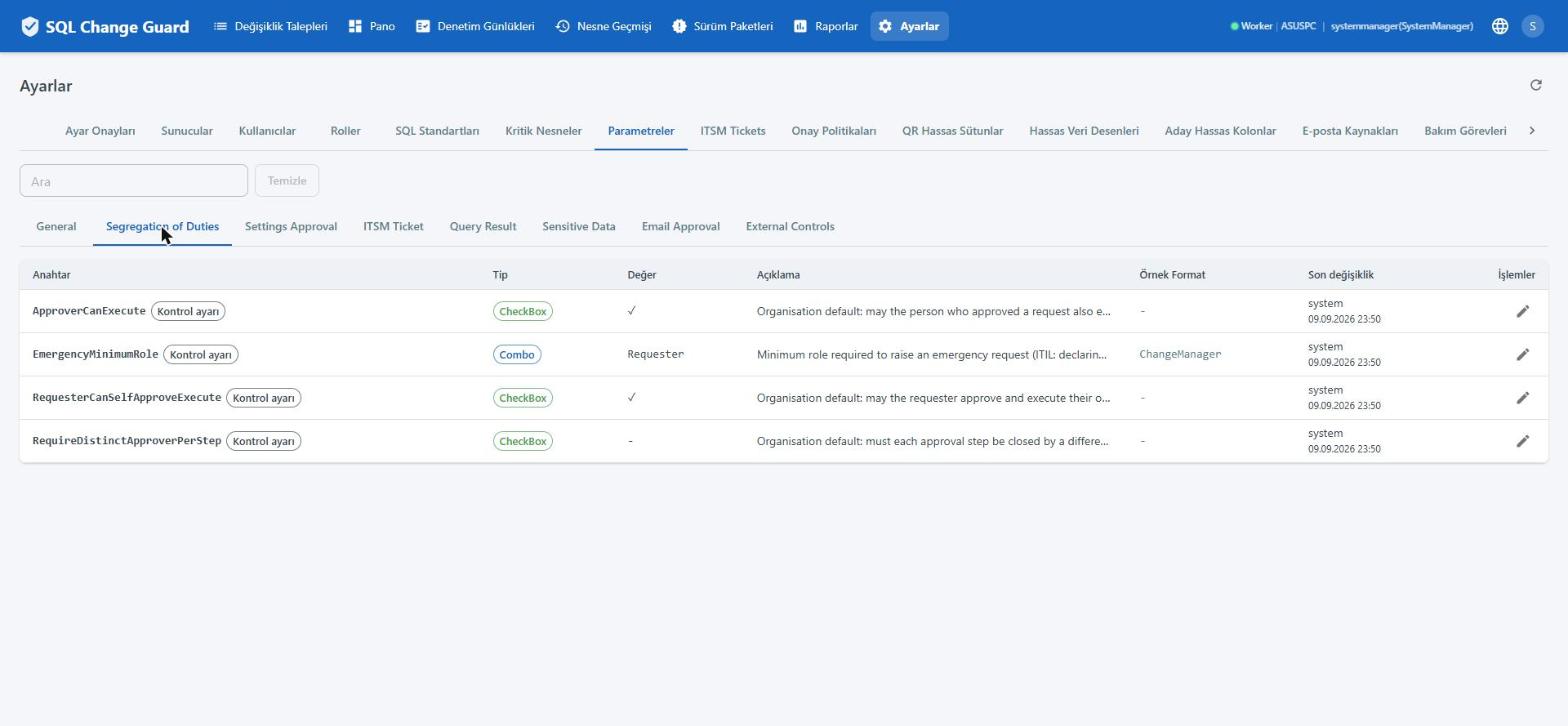
Kapatıldığında talep sahibi kendi talebini ne onaylayabilir ne de çalıştırabilir.When switched off, a requester can neither approve nor execute their own request.
Kapatıldığında bir adımı onaylayan kişi aynı talebi çalıştıramaz.When switched off, whoever closed a step cannot execute that same request.
Açıldığında bir kişi aynı talepte yalnız tek bir adımı kapatabilir.When switched on, one person can close only one step on the same request.
Kurulum varsayılanında görevler ayrılığı gevşektir: talep sahibi kendi talebini onaylayıp çalıştırabilir ve onaylayan çalıştırabilir; Yönetişim Kurulum Kontrolü ekranı bunları ayrı satırlarda gösterir. Bu üç ayarın etkin değeri talep kaydedilirken dondurulur. Sonradan yapılan değişiklik, karara bağlanmış talepleri geriye dönük değiştirmez. The installation default is permissive: a requester may approve and execute their own request and an approver may execute; the Governance Setup Check screen shows each of these on its own line. The effective value of these three settings is frozen when the request is saved. A later change does not rewrite requests that were already decided.
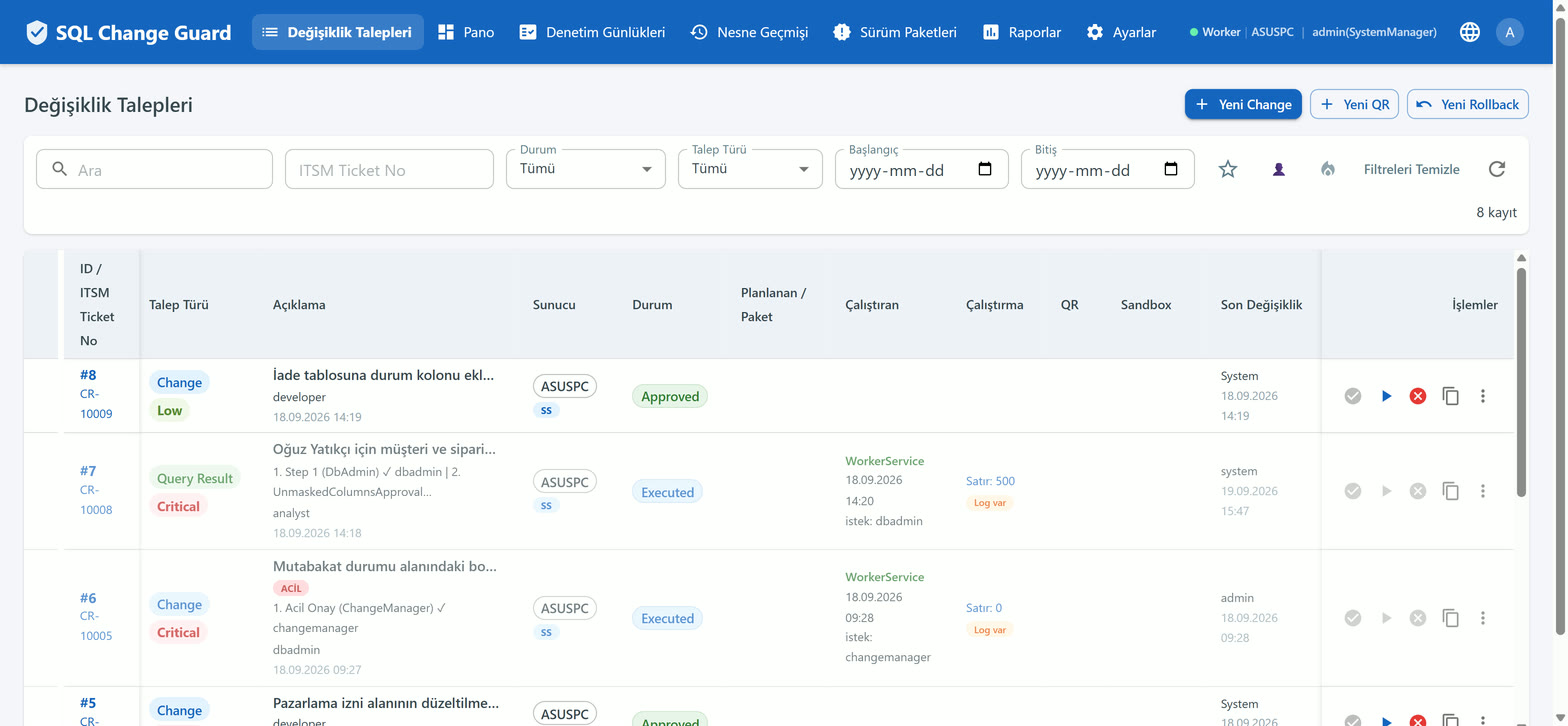
Yetkili bir kullanıcı talebi çalıştırır ya da ileri bir zamana kurar. Sunucu bazında otomatik çalıştırma açılabilir; ancak asla atlanamaz bir kural tetiklendiyse makine çalıştırmaz, bir insanın düğmeye basması gerekir.An authorised user executes the request or schedules it for later. Automatic execution can be enabled per server, but if a never skip rule was triggered the machine will not run it and a person has to press the button.
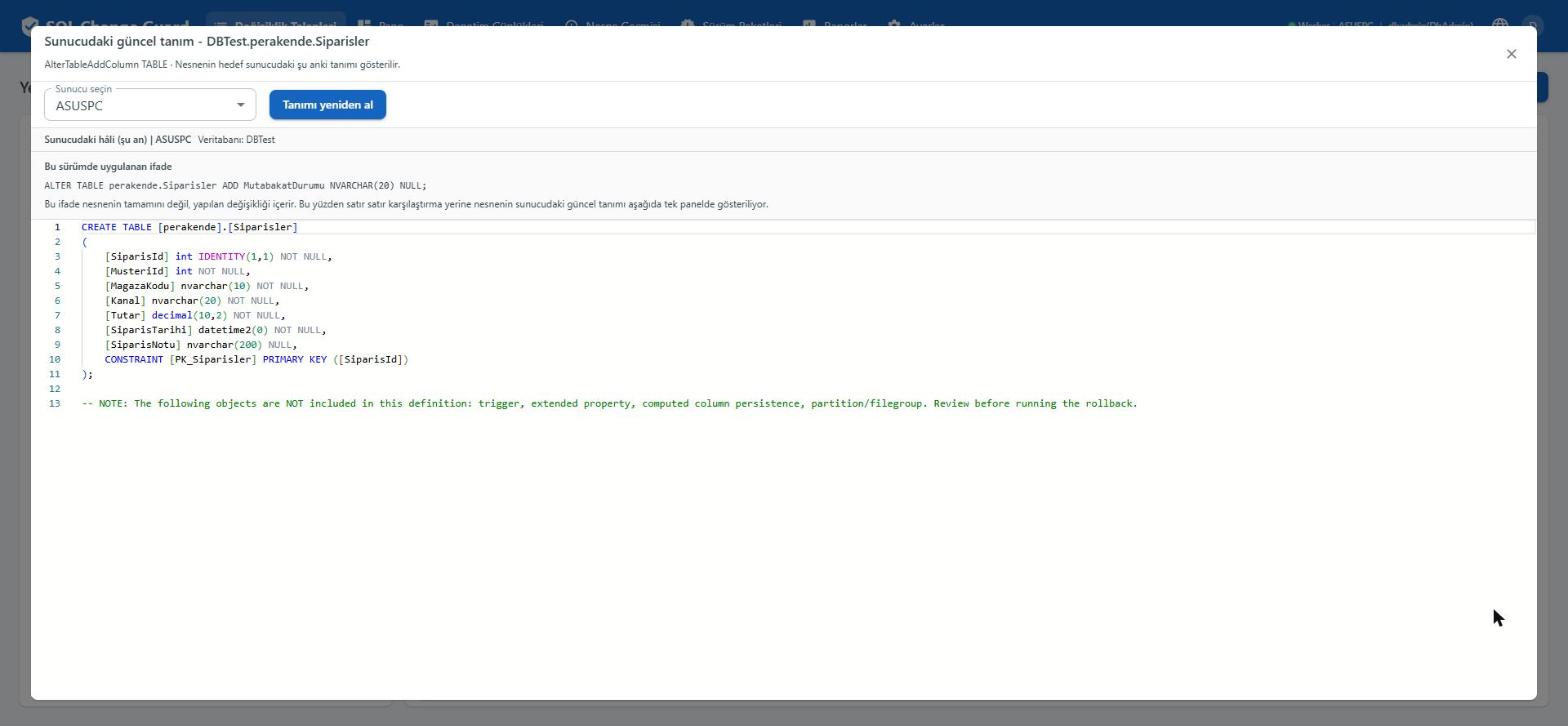
Ürün betikten geri alma betiği üretebilir. Sunucu bazında "geri alma olmadan çalıştırılamaz" kuralı konabilir. Betik, üretim dışı bir sunucuda, sonunda geri alınan bir transaction içinde denenebilir ve sonuç talebe iliştirilir. Bu deneme üretim koşullarının tam benzetimi değildir; Oracle'da DDL, DCL ya da TRUNCATE içeren talep denenemez.The product can generate a rollback script from the original. A server can be marked so that nothing runs without one. A script can also be tried on a non production server inside a transaction that is rolled back at the end, and the result is attached to the request. The trial is not a full simulation of production; on Oracle a request containing DDL, DCL or TRUNCATE cannot be tried.
Kapsamı açık söyleyelim. Otomatik üretim nesne tanımı değişiklikleri içindir: tablo, kolon, indeks, görünüm, saklı yordam ve benzerlerinde sunucudaki güncel tanım okunup ters yönlü betik hazırlanır. Veri değiştiren ifadelerde (INSERT, UPDATE, DELETE, MERGE, TRUNCATE) ve yordam çağrılarında (EXEC) eski satır değerleri betikten çıkarılamaz ve ürün bugün çalıştırmadan önce etkilenecek satırların kopyasını almaz. Bu durumda geri alma betiği elle hazırlanıp talebe iliştirilir ve sunucu ayarı bunu zorunlu tutabilir. Bilinen sınırlar: silinen bir tablo katalogdan yeniden kurulurken SQL Server ve PostgreSQL'de hesaplanan kolonun ifadesi gelmez, kolon düz kolon olarak kurulur (Oracle'da bu kayıp yoktur); tablonun tetikleyicileri de yeniden kurulmaz. Üretilen betiğin sonunda kapsam dışı kalanlar not olarak yazar ve betik onaydan önce gözden geçirilmelidir.Let us be explicit about the scope. Automatic generation covers object definition changes: for tables, columns, indexes, views, procedures and the like, the current definition is read from the server and the reversing script is prepared. For statements that change data (INSERT, UPDATE, DELETE, MERGE, TRUNCATE) and for procedure calls (EXEC) the previous row values cannot be derived from the script, and today the product does not copy the affected rows before execution. In those cases the rollback script is written by hand and attached to the request, and a server setting can make that mandatory. Known limits: when a dropped table is rebuilt from the catalogue, the expression of a computed column is not carried over on SQL Server and PostgreSQL and the column comes back as a plain column (Oracle has no such loss); the table's triggers are not rebuilt either. The generated script lists what was left out in a note at the end, and the script should be reviewed before approval.
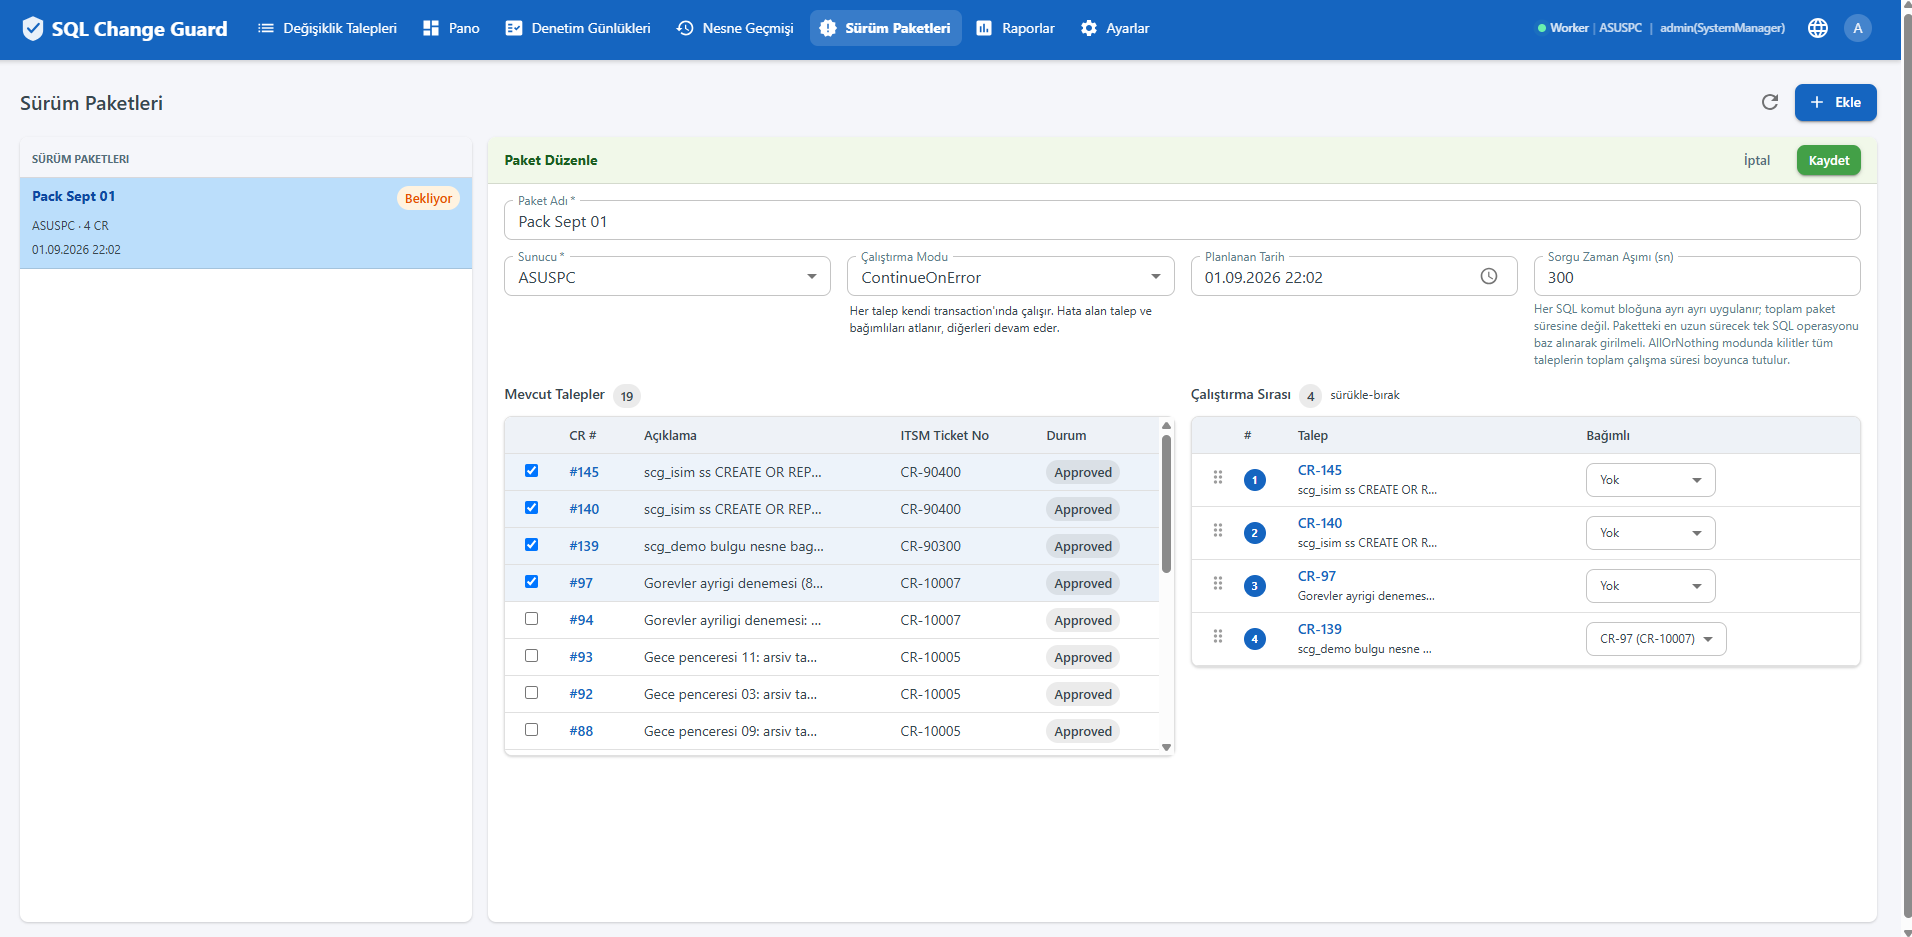
Birden çok talep tek pakette toplanıp sırayla çalıştırılabilir. Pakete alınan talep artık paketin denetimindedir; tek tek düzenleme ve çalıştırma kapanır.Several requests can be gathered into one package and run in order. A request inside an active package is governed by the package; editing and running it on its own is disabled.
Acil talep ayrı bir acil durum politikasına yönlendirilir. Gerekçe zorunludur, acil yol yalnız tanımlı bir rol seviyesinden itibaren açılır ve acil politikanın en az bir atlanamaz onay adımı içermesi zorunludur.An emergency request is routed to a separate emergency policy. A justification is mandatory, the emergency route opens only from a defined role level upward, and an emergency policy must contain at least one non skippable approval step.